Hackers are exploiting a server vulnerability with a severity of 9.8 out of 10

Hackers are exploiting a server vulnerability with a severity of 9.8 out of 10
Getty Images

In a development security pros feared, attackers are actively targeting yet another set of critical server vulnerabilities that leave corporations and governments open to serious network intrusions.

The vulnerability this time is in BIG-IP, a line of server appliances sold by Seattle-based F5 Networks. Customers use BIG-IP servers to manage traffic going into and out of large networks. Tasks include load balancing, DDoS mitigation, and web application security.

Last week, F5 disclosed and patched critical BIG-IP vulnerabilities that allow hackers to gain complete control of a server. Despite a severity rating of 9.8 out of 10, the security flaws got overshadowed by a different set of critical vulnerabilities Microsoft disclosed and patched in Exchange server a week earlier. Within a few days of Microsoft’s emergency update, tens of thousands of Exchange servers in the US were compromised.

Day of reckoning

When security researchers weren’t busy attending to the unfolding Exchange mass compromise, many of them warned that it was only a matter of time before the F5 vulnerabilities also came under attack. Now, that day has come.

Researchers at security firm NCC Group on Friday said they’re “seeing full chain exploitation” of CVE-2021-22986, a vulnerability that allows remote attackers with no password or other credentials to execute commands of their choice on vulnerable BIG-IP devices.

“After seeing lots of broken exploits and failed attempts, we are now seeing successful in the wild exploitation of this vulnerability, as of this morning,” Rich Warren, Principal Security Consultant at NCC Group and co-author of the blog wrote.

In a blog post NCC Group posted a screenshot showing exploit code that could successfully steal an authenticated session token, which is a type of browser cookie that allows administrators to use a web-based programming interface to remotely control BIG-IP hardware.

“The attackers are hitting multiple honeypots in different regions, suggesting that there is no specific targeting,” Warren wrote in an email. “It is more likely that they are ‘spraying’ attempts across the internet, in the hope that they can exploit the vulnerability before organizations have a chance to patch it.”

He said that earlier attempts used incomplete exploits that were derived from the limited information that was available publicly.

Security firm Palo Alto Networks, meanwhile, said that CVE-2021-22986 was being targeted by a devices infected with a variant of the open-source Mirai malware. The tweet said the variant was “attempting to exploit” the vulnerability, but it wasn’t clear if the attempts were successful.

Other researchers reported Internet-wide scans designed to locate BIG-IP servers that are vulnerable.

CVE-2021-22986 is only one of several critical BIG-IP vulnerabilities F5 disclosed and patched last week. The severity In part is because the vulnerabilities require limited skill to exploit. But more importantly, once attackers have control of a BIG-IP server, they are more or less inside the security perimeter of the network using it. That means attackers can quickly access other sensitive parts of the network.

As if admins didn’t already have enough to attend to, patching vulnerable BIG-IP servers and looking for exploits should be a top priority. NCC Group provided indicators of compromise in the link above, and Palo Alto Networks has IOCs here.

Update: After this post went live, F5 issued a statement. It read: “We are aware of attacks targeting recent vulnerabilities published by F5. As with all critical vulnerabilities, we advise customers update their systems as soon as possible.”

Meanwhile, NCC Group’s Rich Warren responded to questions I sent earlier. Here’s a partial Q&A:

What does “seeing full chain exploitation” mean? What was NCC Group seeing before, and how does “full chain exploitation” change it?

What we mean is that, previously we were seeing attackers attempting to abuse the SSRF vulnerability in a way which could not work, because an important part of the exploit was not public knowledge, therefore the exploits would fail. Now, attackers have figured out the full details needed to use the SSRF to bypass authentication and obtain authentication tokens. These authentication tokens can then be used to execute commands remotely. So far, we have seen the attackers a) obtain an authentication token, and b) execute commands to dump credentials. We haven’t seen any web-shells being dropped like we did with CVE-2020-5902, yet.

Where, precisely, are you seeing the exploit attempts? Is it in a honeypot, on production servers, somewhere else?

The attackers are hitting multiple honeypots in different regions, suggesting that there is no specific targeting. It is more likely that they are “spraying” attempts across the internet, in the hope that they can exploit the vulnerability before organizations have a chance to patch it. Earlier attempts we saw against our honeypot infrastructure showed that attackers were using incomplete exploits based on limited information that was available in the public domain. This shows that attackers are obviously keen to exploit the vulnerability – even if some of them don’t have the requisite knowledge to engineer their own attack code.

Do you know if the exploits are succeeding in compromising production servers? If yes, what are attackers doing post exploitation?

At the moment we can’t comment on whether the same attackers have been successful against other people’s servers. With regards to post-exploitation activities, we have only seen credential dumping so far.

I’m reading that multiple threat groups are exploiting the vulnerability. Do you know this to be true? If so, how many different threat actors are there?

We’ve not stated that there are multiple attackers. In fact, while we’ve seen multiple successful exploitation attempts from different IPs, all attempts have contained some specific hallmarks which are consistent with the other attempts, suggesting it’s likely the same underlying exploit.

https://arstechnica.com/?p=1751018


Microsoft Defender Antivirus Now Protects Users Against Ongoing Exchange Attacks

Microsoft informed customers on Thursday that Defender Antivirus and System Center Endpoint Protection now provide automatic protection against attacks exploiting the recently disclosed Exchange Server vulnerabilities.

Microsoft has released patches, detailed guidance, and a one-click mitigation tool to ensure that Exchange Server users are protected against attacks. The tech giant has now taken another step to protect customers who haven’t managed to install the available patches but who have Defender deployed on vulnerable servers.

The Exchange vulnerabilities are tracked as CVE-2021-26855, CVE-2021-26857, CVE-2021-26858 and CVE-2021-27065, and they are tracked as ProxyLogon. They can be exploited by an unauthenticated attacker to execute arbitrary code on targeted servers and gain access to emails and other sensitive information.

When Microsoft disclosed the flaws and announced patches in early March, it warned that a threat actor linked to China had been exploiting them in attacks. Roughly one week after disclosure, others reported that several cyberspy and cybercrime groups had started exploiting the vulnerabilities.

On March 12, Microsoft reported that more than 80,000 Exchange servers had still not been updated.

As threat actors increasingly start to target these vulnerabilities, Microsoft has now decided to release a security intelligence update for Defender Antivirus and System Center Endpoint Protection (build 1.333.747.0 or newer), which according to the company “breaks the attack chain by mitigating CVE-2021-26855,” the first vulnerability exploited in the ProxyLogon chain.

List of resources to help incident response teams and IT administrators respond to this global incident.

Microsoft described this as an “interim mitigation” that should help customers protect their systems until they can install the patches.

“Microsoft Defender Antivirus will automatically identify if a vulnerable version of Exchange Server is installed and apply the mitigations the first time the security intelligence update is deployed. The mitigation is deployed once per machine,” Microsoft explained.

Related: At Least 10 Threat Actors Targeting Recent Microsoft Exchange Vulnerabilities

Related: Ransomware Operators Start Targeting Microsoft Exchange Vulnerabilities

Related: Hackers Looking for Exchange Servers Affected by Recently Patched Flaw

view counter

Eduard Kovacs (@EduardKovacs) is a contributing editor at SecurityWeek. He worked as a high school IT teacher for two years before starting a career in journalism as Softpedia’s security news reporter. Eduard holds a bachelor’s degree in industrial informatics and a master’s degree in computer techniques applied in electrical engineering.

Previous Columns by Eduard Kovacs:
Tags:

http://feedproxy.google.com/~r/Securityweek/~3/T2LIwFCaheI/microsoft-defender-antivirus-now-protects-users-against-ongoing-exchange-attacks


Facebook Paid Out $50K for Vulnerabilities Allowing Access to Internal Systems

A researcher says he has earned more than $50,000 from Facebook after discovering vulnerabilities that could have been exploited to gain access to some of the social media giant’s internal systems.

Cybersecurity engineer and bug bounty hunter Alaa Abdulridha revealed in December 2020 that he had earned $7,500 from Facebook for discovering a vulnerability in a service apparently used by the company’s legal department. The researcher said the security hole could have been exploited to reset the password of any account for a web application used internally by Facebook employees.

Internal Facebook app hacked

In a blog post published on Thursday, the researcher said he continued analyzing the same application and once again managed to gain access to it. From there he claimed he was able to launch a server-side request forgery (SSRF) attack and gain access to Facebook’s internal network. Facebook described this as an attacker being able to send HTTP requests to internal systems and read their responses.

“I was able to scan the ports of the local servers and browse the local applications/web apps that the company uses in their infrastructure,” the researcher told SecurityWeek. “I’m sure such a vulnerability in the wrong hands could be escalated to RCE and can pose a huge risk for the company and its customers.”

The social media giant awarded him nearly $50,000 for this second exploit chain.

Abdulridha also claimed the account takeover attack may have allowed a hacker to access accounts for other internal Facebook applications as well, but Facebook told SecurityWeek it had not found any evidence to suggest that the flaw could be escalated to access other internal accounts.

Facebook has clarified that the vulnerabilities reported by Abdulridha actually affected a third-party service designed for signing documents and they impacted anyone using this service, not just Facebook. The company said it worked with the third-party vendor to quickly get the flaws fixed and said it had found no evidence of malicious exploitation, noting that exploiting the weaknesses was a complex task.

The company also pointed out that the first vulnerability only allowed access to accounts within the third-party document signing app, but did not grant access to any employee accounts used for other internal applications.

While the researcher claimed that it took Facebook nearly 6 months to patch the second round of vulnerabilities, the company told SecurityWeek that while the report was only closed in February, the bugs were actually completely fixed — by both Facebook and the third-party vendor — within a few days.

Facebook also said that while it paid out a bug bounty based on the maximum possible impact it could determine, it did not agree with the researcher’s belief that the SSRF vulnerabilities could have been escalated to remote code execution.

Related: Facebook Announces Payout Guidelines for Bug Bounty Program

Related: Facebook Awards Big Bounties for Invisible Post and Account Takeover Vulnerabilities

Related: Facebook Pays $60,000 for Vulnerability in Messenger for Android

view counter

Eduard Kovacs (@EduardKovacs) is a contributing editor at SecurityWeek. He worked as a high school IT teacher for two years before starting a career in journalism as Softpedia’s security news reporter. Eduard holds a bachelor’s degree in industrial informatics and a master’s degree in computer techniques applied in electrical engineering.

Previous Columns by Eduard Kovacs:
Tags:

http://feedproxy.google.com/~r/Securityweek/~3/4qCvsGF0k4U/facebook-paid-out-50k-vulnerabilities-allowing-access-internal-systems


Here’s How Security Flaws in GE Relays Could Be Exploited in Real World Attacks

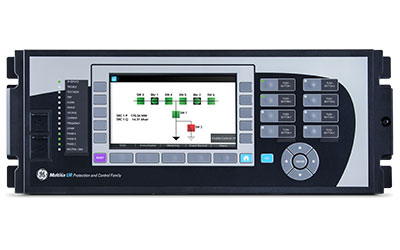
Organizations using Universal Relay (UR) products made by GE’s Grid Solutions have been informed this week that many of the devices in this product line are affected by nearly a dozen vulnerabilities.

Grid Solutions is a GE Renewable Energy business that provides electricity management solutions for the energy sector, including oil and gas, as well as industry and infrastructure organizations.

Advisories published this week by the U.S. Cybersecurity and Infrastructure Security Agency (CISA) and GE Grid Solutions (account required) inform customers that more than a dozen UR protection and control relays are impacted by a series of vulnerabilities to which 10 different CVE identifiers have been assigned. The vendor has released firmware updates that should patch the vulnerabilities.

GE grid relay vulnerabilitiesThe flaws are related to inadequate encryption of communications, exposure of potentially sensitive information, cross-site scripting (XSS) attacks, denial-of-service (DoS) attacks, unauthorized firmware uploading, the inability to disable a factory service mode, and the presence of hardcoded credentials in the bootloader. More than half of the vulnerabilities have a severity rating of high or critical.

Researchers from SCADA-X, Verve Industrial, VuMetric and the Department of Energy’s Cyber Testing for Resilient Industrial Control Systems (CyTRICS) program have been credited for finding the security holes.

Ron Brash, director of cyber security insights at ICS management and cybersecurity provider Verve Industrial Protection, told SecurityWeek that he has identified two or possibly three of the vulnerabilities — he says it’s difficult to say exactly due to multiple disclosures and some likely overlap. These include flaws that can be exploited to upload malicious firmware to the device, obtain potentially sensitive information, and access a device or disrupt it.

According to Brash, exploitation of these vulnerabilities requires direct or network access to the targeted system.

“Generally these devices are not found on the Internet directly unless someone has not applied any secure deployment strategies, or has inadvertently misconfigured various network infrastructure devices/security apparatuses,” he explained.

Learn more about vulnerabilities in industrial systems at SecurityWeek’s ICS Cyber Security Conference and SecurityWeek’s Security Summits virtual event series

In terms of impact, the expert pointed out that while the vulnerable relays are used within the energy industry, they are not limited to the “grid.”

“For example, a mine may be generating power, and these types of devices might be present,” Brash explained. “This can mean that the results or motivations of what ‘an attacker could do’ might be situationally dependent, or require specific contexts. Therefore, in continuation of the example, if your mine needs energy to keep liquids unfrozen (e.g., washes, effluent management systems, etc), and the mine is located in Canada’s North, then you might have a BIG problem during winter. Secondly, if you can get access to these devices, and upload your own logic or firmware, then you can effectively brick them, upload malicious functionality, and the consequences will be highly negative.”

He added, “I don’t wish to speculate as to the motives, or what could be accomplished by an attacker, but if exploited at scale (which by the way, takes a great level of skill, budget, and organization) – nothing positive would result.”

Contacted by SecurityWeek, GE said it’s currently not aware of any attacks exploiting these vulnerabilities.

“GE was made aware of vulnerabilities related to GE’s Grid Solutions’ Universal Relay (UR) family products and immediately worked to assess any potential impact and remediate the reported vulnerabilities. GE’s UR firmware Version 8.10 and greater resolve the identified vulnerabilities, and we encourage our customers to visit the Grid Solutions customer portal and/or the CISA Advisory for additional information and mitigation recommendations,” said a GE spokesperson.

Related: Critical Flaw in GE Protection Relays Exposes Power Grid

Related: Over 100 GE Healthcare Devices Affected by Critical Vulnerability

Related: Open Source Tool Helps Organizations Secure GE CIMPLICITY HMI/SCADA Systems

view counter

Eduard Kovacs (@EduardKovacs) is a contributing editor at SecurityWeek. He worked as a high school IT teacher for two years before starting a career in journalism as Softpedia’s security news reporter. Eduard holds a bachelor’s degree in industrial informatics and a master’s degree in computer techniques applied in electrical engineering.

Previous Columns by Eduard Kovacs:
Tags:

http://feedproxy.google.com/~r/Securityweek/~3/Z6dFJUL__NY/heres-how-recently-patched-ge-relay-flaws-could-be-exploited-real-world-attacks


“Expert” hackers used 11 zerodays to infect Windows, iOS, and Android users

The word ZERO-DAY is hidden amidst a screen filled with ones and zeroes.

A team of advanced hackers exploited no fewer than 11 zeroday vulnerabilities in a nine-month campaign that used compromised websites to infect fully patched devices running Windows, iOS, and Android, a Google researcher said.

Using novel exploitation and obfuscation techniques, a mastery of a wide range of vulnerability types, and a complex delivery infrastructure, the group exploited four zerodays in February 2020. The hackers’ ability to chain together multiple exploits that compromised fully patched Windows and Android devices led members of Google’s Project Zero and Threat Analysis Group to call the group “highly sophisticated.”

Not over yet

On Thursday, Project Zero researcher Maddie Stone said that, in the eight months that followed the February attacks, the same group exploited seven more previously unknown vulnerabilities, which this time also resided in iOS. As was the case in February, the hackers delivered the exploits through watering-hole attacks, which compromise websites frequented by targets of interest and add code that installs malware on visitors’ devices.

In all the attacks, the watering-hole sites redirected visitors to a sprawling infrastructure that installed different exploits depending on the devices and browsers visitors were using. Whereas the two servers used in February exploited only Windows and Android devices, the later attacks also exploited devices running iOS. Below is a diagram of how it worked:

The ability to pierce advanced defenses built into well-fortified OSes and apps that were fully patched—for example, Chrome running on Windows 10 and Safari running on iOSA—was one testament to the group’s skill. Another testament was the group’s abundance of zerodays. After Google patched a code-execution vulnerability the attackers had been exploiting in the Chrome renderer in February, the hackers quickly added a new code-execution exploit for the Chrome V8 engine.

In a blog post published Thursday, Stone wrote:

The vulnerabilities cover a fairly broad spectrum of issues—from a modern JIT vulnerability to a large cache of font bugs. Overall each of the exploits themselves showed an expert understanding of exploit development and the vulnerability being exploited. In the case of the Chrome Freetype 0-day, the exploitation method was novel to Project Zero. The process to figure out how to trigger the iOS kernel privilege vulnerability would have been non-trivial. The obfuscation methods were varied and time-consuming to figure out.

In all, Google researchers gathered:

  • 1 full chain targeting fully patched Windows 10 using Google Chrome
  • 2 partial chains targeting 2 different fully patched Android devices running Android 10 using Google Chrome and Samsung Browser, and
  • RCE exploits for iOS 11-13 and privilege escalation exploit for iOS 13

The seven zerodays were:

  • CVE-2020-15999 – Chrome Freetype heap buffer overflow
  • CVE-2020-17087 – Windows heap buffer overflow in cng.sys
  • CVE-2020-16009 – Chrome type confusion in TurboFan map deprecation
  • CVE-2020-16010 – Chrome for Android heap buffer overflow
  • CVE-2020-27930 – Safari arbitrary stack read/write via Type 1 fonts
  • CVE-2020-27950 – iOS XNU kernel memory disclosure in mach message trailers
  • CVE-2020-27932 – iOS kernel type confusion with turnstiles

Piercing defenses

The complex chain of exploits is required to break through layers of defenses that are built into modern OSes and apps. Typically, the series of exploits are needed to exploit code on a targeted device, have that code break out of a browser security sandbox, and elevate privileges so the code can access sensitive parts of the OS.

Thursday’s post offered no details on the group responsible for the attacks. It would be especially interesting to know if the hackers are part of a group that’s already known to researchers or if it’s a previously unseen team. Also useful would be information about the people who were targeted.

The importance of keeping apps and OSes up to date and avoiding suspicious websites still stands. Unfortunately, neither of those things would have helped the victims hacked by this unknown group.

https://arstechnica.com/?p=1750760


Facebook Now Lets Mobile Users Secure Accounts with Security Keys

Social media and advertising giant Facebook today announced that it is now allowing mobile users to secure their accounts with the help of security keys.

Available for Facebook’s desktop users since 2017, the authentication method requires that the user confirm authentication requests with the help of a physical security key.

This additional authentication step is meant to significantly increase account protection, as it relies on the use of a physical device that an attacker is assumed to never have access to.

“Starting today, you can set up two-factor authentication and log into Facebook on iOS and Android mobile devices using a security key, available to anyone in the world,” Facebook announced.

Two-factor authentication (2FA) has evolved from codes sent via SMS or email to the use of authenticator applications and security keys, making it increasingly difficult for a threat actor to come in the possession of both the account password and the second factor.

Since 2017, Facebook has been providing users the option to enable 2FA and choose physical security keys as the second authentication factor, with that feature now available for iOS and Android users as well.

Users who may need such strong authentication protection are those most exposed to malicious attacks, including public figures, politicians, journalists, and human rights defenders, among others.

“We strongly recommend that everyone considers using physical security keys to increase the security of their accounts, no matter what device you use,” Facebook says.

Security keys can be connected either via Bluetooth or can be directly plugged into phones.

To enable the use of security keys as the authentication method, Facebook users should head over to the Security and Login section of the Settings menu.

The social platform also says it plans to expand the availability of its Facebook Protect program to include additional at-risk groups, alongside political campaigns and candidates.

Related: Twitter Users Can Now Secure Accounts With Multiple Security Keys

Related: New YubiKey 5C NFC Security Key Brings NFC, USB-C Connections 

view counter

Ionut Arghire is an international correspondent for SecurityWeek.

Previous Columns by Ionut Arghire:
Tags:

http://feedproxy.google.com/~r/Securityweek/~3/14vNnXceNuw/facebook-now-lets-mobile-users-secure-accounts-security-keys


Healthcare IoT Security Firm Cylera Closes $10 Million Series A Round

Healthcare IoT cybersecurity and intelligence provider Cylera today announced that it has raised $10 million in Series A funding. To date, the company has secured $17 million in funding.

Founded in 2017 and headquartered in New York City, Cylera seeks to protect both healthcare organizations and patients, providing a security and analytics platform that aims to deliver asset management, risk analysis, and threat detection for IoT, ICS, and IoMT (Internet of Medical Things).

Cylera seeks to secure the entire connected environment, providing insights and recommendations that simplify response, accelerate remediation, and improve the decision making process.

Cylera’s Series A funding round was led by Concord Health Partners and Maverick Ventures. Previous investors include Dreamit Ventures, Great Oaks Venture Capital, Red Bear Angels, and Samsung NEXT.

The funds will help the company expand to new global markets, as well as make its technology available for new verticals. Furthermore, Cylera plans to expand its research and development, customer success, channel support, and sales and marketing teams.

“Over the past year there has been a further acceleration of the digitalization and adoption of IoT devices across hospitals, pharmaceutical companies, biotech, life sciences and manufacturing in an effort to decrease operational risk and increase efficiencies. […] With our latest round of funding, Cylera is fueling the next phase of innovation to safeguard organizations against attacks on connected devices,” Cylera co-founder and CEO Timur Ozekcin said.

Related: HD Moore Banks $5M Funding for Rumble Asset Management

Related: Aqua Security Hits Unicorn Status After $135 Million Funding Round

Related: Cyber Insurance Company Coalition Raises $175 Million

view counter

Ionut Arghire is an international correspondent for SecurityWeek.

Previous Columns by Ionut Arghire:
Tags:

http://feedproxy.google.com/~r/Securityweek/~3/a5KE8ovM3a0/healthcare-iot-security-firm-cylera-closes-10-million-series-round


Chinese Cyberspies Target Telecom Companies in America, Asia, Europe

China-linked cyber-espionage group Mustang Panda is targeting telecommunications companies in Asia, Europe, and the United States for espionage purposes, according to a warning from security researchers at McAfee.

Also referred to as RedDelta and TA416, the threat actor has been previously associated with the targeting of entities in connection with the Vatican – Chinese Communist Party diplomatic relations, along with some entities in Myanmar.

The new malware attacks, McAfee says, employ the same tactics, techniques and procedures (TTPs) previously associated with Mustang Panda. The initial vector of infection hasn’t been identified, but the researchers believe that victims were being lured to a fake website crafted to mimic the legitimate career site for Chinese tech giant Huawei.

The first stage of the attack leverages a fake Flash application and a phishing page mimicking the original website, while the second stage is a .Net payload executed to further compromise the machine through downloading and managing backdoors. A Cobalt Strike beacon payload is delivered as a third stage.

Referred collectively as Operation Diànxùn, the new attacks were targeted at telecommunication companies in based in Southeast Asia, Europe, and the United States. The adversary, McAfee says, shows strong interest in German, Vietnamese, and Indian telecommunication companies.

“Combined with the use of the fake Huawei site, we believe with a high level of confidence that this campaign was targeting the telecommunication sector. We believe with a moderate level of confidence that the motivation behind this specific campaign has to do with the ban of Chinese technology in the global 5G roll-out,” McAfee says.

The campaign, the researchers note, is believed to have been aimed at the theft of sensitive or secret information related to 5G technology. McAfee also notes that it has no evidence that Huawei was knowingly involved in these attacks.

Related: China-Linked Hackers Exploited SolarWinds Flaw in U.S. Government Attack: Report

Related: Facebook Says Fake Accounts From China Aimed at US Politics

view counter

Ionut Arghire is an international correspondent for SecurityWeek.

Previous Columns by Ionut Arghire:
Tags:

http://feedproxy.google.com/~r/Securityweek/~3/L5Vth0BDCV0/chinese-cyberspies-target-telecom-companies-america-asia-europe


HD Moore Banks $5M Funding for Rumble Asset Management Startup

Network and asset discovery provider Rumble this week announced that it has raised $5 million in VC funding. The round was led by Jon Sakoda and Dan Nguyen-Huu at Cisco-backed Decibel Partners.

The round also saw participation from Duo Security co-founder and CTO Jon Oberheide, Demisto (acquired by Palo Alto Networks) founders Slavik Markovich and Rishi Bhargava, Phantom  Cyber (acquired by Splunk) founder and CEO Oliver Friedrichs, Thinkst Canary founder Haroon Meer, and StoneMill Ventures founder Michael Sutton.

Founded by H.D. Moore, who is best known for creating Metasploit and who also started Rapid7’s Project Sonar, Rumble officially launched in October 2019, after a six-month beta period. At the end of 2020, the company had over 100 paying customers.

The Rumble platform has been designed to inventory inventories IT and OT environments to help with attack surface reduction and incident response.

Rumble’s Explorer scanner was designed to identify outdated and orphaned devices and rogue RDP ports, as well as for the discovery of public-private network bridges, thus increasing security teams’ visibility into enterprise environments.

The new funds, Rumble says, will help it expand the enterprise capabilities of its platform and also accelerate its go-to-market engine.

The funding round was accompanied by Rumble’s 2.0 release, which features ServiceNow ITOM CMDB integration, new discovery modes to identify active subnets and hosts, automated monitoring, expanded API capabilities, and more.

“Most security teams have been trying to get asset inventory data from solutions that weren’t designed for it, such as vulnerability scanners and EDR agents. These solutions weren’t created with that goal in mind, so the data is often spotty, either because it doesn’t properly identify the device or misses it altogether,” HD Moore commented.

Related: Authentication Provider LoginID Raises $6 Million in Seed Funding

Related: 1Kosmos Emerges from Stealth Mode With $15 Million in Funding

Related: Data Privacy Startup TripleBlind Raises $8.2 Million in Seed Funding

view counter

Ionut Arghire is an international correspondent for SecurityWeek.

Previous Columns by Ionut Arghire:
Tags:

http://feedproxy.google.com/~r/Securityweek/~3/wSgUbfqQkx8/hd-moore-banks-5m-funding-rumble-asset-management-startup


Recorded Future Buys Fraud Analytics Startup Gemini Advisory

Threat Intelligence Firm Recorded Future Buys Company Started by Former Employee in $52 Million Deal

Threat intelligence data broker Recorded Future has acquired fraud analytics startup Gemini Advisory as part of a strategic push to expand into the financial services and payment processing markets.

The cash and stock deal is valued at $52 million and comes less than a year after Recorded Future was itself acquired in a $780 million transaction.

Recorded Future expects the Gemini Advisory deal to provide tools and expertise to sell the “most comprehensive intelligence platform” with “the visibility to act at the speed of the adversary to mitigate cyber risk and fraud.”

Upon acquisition, Gemini Advisory will operate as an independent business unit inside of Recorded Future.   

Gemini Advisory is the brainchild of former FBI consultant Andrei Barysevi, who left Recorded Future three years ago to create the new company. 

“In a short time, Gemini Advisory has become a leader in the fraud space with unique offerings in both payment card intelligence and merchant fraud intelligence,” said Recorded Future CEO Christopher Ahlberg. 

“As we continue to execute on our mission to deliver a modular intelligence platform, joining forces with Gemini Advisory expands the value we deliver for customers across enterprise security and fraud,” he added.

Recorded Future itself was acquired by private equity firm Insight Partners for $780 million in a cash deal announced in May 2019.

Related: Recorded Future Acquired for $780M

Related: Recorded Future Adds Third-Party Risk to Threat Intel Platform

view counter

Previous Columns by SecurityWeek News:
Tags:

http://feedproxy.google.com/~r/Securityweek/~3/F1Dvt4680Jo/recorded-future-buys-fraud-analytics-startup-gemini-advisory