A phishing email campaign detailed earlier this month is expanding with the use of additional email services to hide malicious intent, according to a warning from software giant Microsoft.
Dubbed‘Compact’ Campaign, the operation has been ongoing since December 2020, targeting thousands of users. In early March, researchers with the WMC Global Threat Intelligence Team estimated that more than 400,000 Outlook Web Access and Office 365 credentials had been compromised in multiple, connected campaigns.
At the time, the researchers revealed that the adversary behind the campaign was leveraging trusted domains to ensure that phishing emails successfully bypass email protections.
Compromised accounts at the SendGrid email delivery service were used to send many of the emails. After the researchers and SendGrid started terminating the sending accounts, the threat actor switched to MailGun to send the phishing messages.
Now, Microsoft says that the phishing messages are relying on compromised accounts on email marketing services and leverage configuration settings to bypass phishing protections that organizations might have in place.
In addition to SendGrid, the tech giant reveals, the campaign’s operators abused Amazon SES last year, and started leveraging Mailgun for the same purposes since January.
“Microsoft Defender for Office 365 data shows that this phishing operation is still active today and continues to expand,” the company said on Twitter.
“The attackers abuse another legitimate service to further mask the malicious intent of their phishing emails. To evade domain reputation-based solutions, they use Appspot to create multiple unique phishing URLs per recipient,” the tech giant added.
Microsoft also notes that Appspot has been notified on the abuse, and that the company has already confirmed that the reported URLs are malicious. Appspot already took action against the offending projects and is working with Microsoft on tracking this operation.
Some of the phishing emails used in these attacks masquerade as notifications from video conferencing services, while recent attacks spoof security solutions and productivity tools, Microsoft reveals.
“Because this campaign uses compromised email marketing accounts, we strongly recommend orgs to review mail flow rules for broad exceptions that may be letting phishing emails through,” the company concludes.
Vulnerabilities in TBox RTUs Can Expose Industrial Organizations to Remote Attacks
UK-based industrial automation company Ovarro recently patched a series of vulnerabilities in its TBox remote terminal units (RTUs). Cybersecurity experts say these flaws could pose a serious risk to organizations.
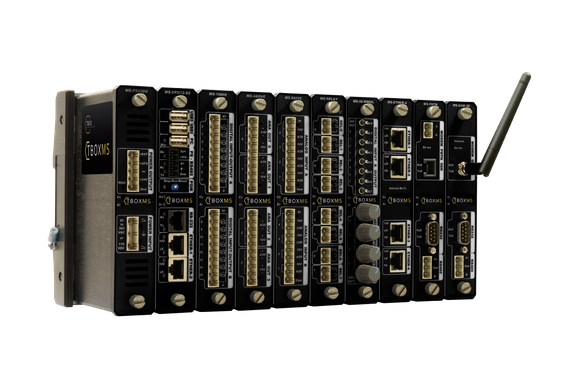
Ovarro’s TBox RTUs are described by the vendor as a remote telemetry solution for remote automation and monitoring of critical assets. These devices are used worldwide, including in the water, oil and gas, power, transportation and process industries.
Researchers at industrial cybersecurity firm Claroty discovered last year that the TBox RTUs, as well as the associated TWinSoft engineering software, are affected by five types of vulnerabilities.
Information about the vulnerabilities — all of which have been rated “high severity” — is available in a blog post published by Claroty and advisories released by the U.S. Cybersecurity and Infrastructure Security Agency (CISA) and Ovarro.
The vulnerabilities can allow an attacker to bypass protection features, cause a denial-of-service (DoS) condition, and execute arbitrary code on a targeted device.
“The risks associated with these flaws threaten not only the integrity of automation processes, but also, in some cases public safety,” Claroty said in its blog post. “Using these security shortcomings, we were able to find web-based interfaces, similar to HMIs, that monitor process levels and other industrial activity. We’ve seen in the past what could go wrong when such an interface is exposed to the internet without security; the fact such interfaces are exposed online removes many barriers to entry for adversaries of all types.”
The company has conducted a search for TBox RTUs and discovered that more than 62% of the systems exposed to the internet did not require authentication.
Claroty reported last month that the number of vulnerabilities discovered in industrial control system (ICS) products in 2020 increased significantly compared to previous years. The company said nearly 900 flaws were disclosed last year.
Eduard Kovacs (@EduardKovacs) is a contributing editor at SecurityWeek. He worked as a high school IT teacher for two years before starting a career in journalism as Softpedia’s security news reporter. Eduard holds a bachelor’s degree in industrial informatics and a master’s degree in computer techniques applied in electrical engineering.
Ransomware operators are piling on already hacked Exchange servers
Microsoft Exchange servers compromised in a first round of attacks are getting infected for a second time by a ransomware gang that is trying to profit from a rash of exploits that caught organizations around the world flat-footed.
The ransomware—known as Black Kingdom, DEMON, and DemonWare—is demanding $10,000 for the recovery of encrypted data, security researchers said. The malware is getting installed on Exchange servers that were previously infected by attackers exploiting a critical vulnerability in the Microsoft email program. Attacks started while the vulnerability was still a zero-day. Even after Microsoft issued an emergency patch, as many as 100,000 servers that didn’t install it in time were infected.
Opportunity knocks
The hackers behind those attacks installed a web shell that allowed anyone who knew the URL to completely control the compromised servers. Black Kingdom was spotted last week by Security firm SpearTip. Marcus Hutchins, a security researcher at security firm Kryptos Logic, reported on Sunday that the malware didn’t actually encrypt files.
Someone just ran this script on all vulnerable Exchange servers via ProxyLogon vulnerability. It claims to be BlackKingdom “Ransomware”, but it doesn’t appear to encrypt files, just drops a ransom not to every directory. pic.twitter.com/POYlPYGjsz
On Tuesday morning, Microsoft Threat Intelligence Analyst Kevin Beaumont reported that a Black Kingdom attack “does indeed encrypt files.
BlackKingdom ransomware on my personal servers. It does indeed encrypt files. They exclude c:\windows, however my storage drivers were in a different folder and it encrypted those… meaning the server doesn’t boot any more. If you’re reading BlackKingdom, exclude *.sys files pic.twitter.com/nUVUJTbcGO
Black Kingdom was spotted last June by security firm RedTeam. The ransomware was taking hold of servers that failed to patch a critical vulnerability in the Pulse VPN software. Black Kingdom also made an appearance at the beginning of last year.
Brett Callow, a security analyst at Emsisoft, said it wasn’t clear why one of the recent Black Kingdom attacks failed to encrypt data.
“The initial version encrypted files, while a subsequent version simply renamed them,” he wrote in an email. “Whether both versions are being simultaneously operated is not clear. Nor is it clear why they altered their code—perhaps because the renaming (fake encryption) process would not be detected or blocked by security products?”
He added that one version of the ransomware is using an encryption method that in many cases allows the data to be restored without paying a ransom. He asked that the method not be detailed to prevent the operators of the ransomware from fixing the flaw.
Patching isn’t enough
Neither Arete nor Beaumont said if Black Kingdom attacks were hitting servers that had yet to install Microsoft’s emergency patch or if the attackers were simply taking over poorly secured web shells installed earlier by a different group.
Two weeks ago, Microsoft reported that a separate strain of ransomware named DearCry was taking hold of servers that had been infected by Hafnium. Hafnium is the name the company gave to state-sponsored hackers in China that were the first to use ProxyLogon, the name given to a chain of exploits that gains complete control over vulnerable Exchange servers.
Security firm SpearTip, however, said that the ransomware was targeting servers “after initial exploitation of the available Microsoft exchange vulnerabilities.” The group installing the competing DearCry ransomware also piggybacked.
Black Kingdom comes as the number of vulnerable servers in the US dropped to less than 10,000, according to Politico, which cited a National Security Council spokesperson. There were about 120,000 vulnerable systems earlier this month.
As the follow-on ransomware attacks underscore, patching servers isn’t anywhere near a full solution to the ongoing Exchange server crisis. Even when severs receive the security updates, they can still be infected with ransomware if any web shells remain.
Microsoft is urging affected organizations that don’t have experienced security staff to run this one-click mitigation script.
https://arstechnica.com/?p=1751780
Purple Fox Malware Squirms Like a Worm on Windows
Malware hunters at Guardicore are warning that an aggressive botnet operator has turned to SMB password brute-forcing to infect and spread like a worm across the Microsoft Windows ecosystem.
The malware campaign, dubbed Purple Fox, has been active since at least 2018 and the discovery of the new worm-like infection vector is yet another sign that consumer-grade malware continues to reap profits for cybercriminals.
According to Guardicore researcher Amit Serper, the Purple Fox operators primarily used exploit kits and phishing emails to build botnets for crypto-mining and other nefarious uses.
Now, the new SMB brute-force method is being combined with rootkit capabilities to hide and spread widely across internet-facing Windows computers with weak passwords.
“Throughout the end of 2020 and the beginning of 2021, Guardicore Global Sensors Network (GGSN) detected Purple Fox’s novel spreading technique via indiscriminate port scanning and exploitation of exposed SMB services with weak passwords and hashes,” Serper explained.
Serper said May 2020 saw a “significant amount of malicious activity” where the number of infections climbed by roughly 600% and amounted to a total of 90,000 attacks.
Serper’s blog, which contains IOCs to help defenders hunt for signs of infection, explains the aggressiveness of the malware operator:
“While it appears that the functionality of Purple Fox hasn’t changed much post exploitation, its spreading and distribution methods – and its worm-like behavior – are much different than described in previously published articles. Throughout our research, we have observed an infrastructure that appears to be made out of a hodge-podge of vulnerable and exploited servers hosting the initial payload of the malware, infected machines which are serving as nodes of those constantly worming campaigns, and server infrastructure that appears to be related to other malware campaigns.
Serper’s team at Guardicore warned that the attackers are hosting various MSI packages on nearly 2,000 servers, most of which are compromised machines which were repurposed to host malicious payloads.
“We have established that the vast majority of the servers, which are serving the initial payload, are running on relatively old versions of Windows Server running IIS version 7.5 and Microsoft FTP, which are known to have multiple vulnerabilities with varying severity levels,” Guardicore said in a technical blog post.
The company found the campaign spreading via two distinct mechanisms — a worm payload after a victim machine is compromised through a vulnerable exposed service (such as SMB); or the worm payload is being sent via email through a phishing campaign.
The company is encouraging malware hunters to use public indicators of compromise to find signs of malicious activity related to this threat.
Ryan Naraine is Editor-at-Large at SecurityWeek and host of the popular Security Conversations podcast series. Ryan is a journalist and cybersecurity strategist with more than 20 years experience covering IT security and technology trends. He is a regular speaker at cybersecurity conferences around the world.
Ryan has built security engagement programs at major global brands, including Intel Corp., Bishop Fox and Kaspersky GReAT. He is a co-founder of Threatpost and the global SAS conference series. Ryan’s career as a journalist includes bylines at major technology publications including Ziff Davis eWEEK, CBS Interactive’s ZDNet, PCMag and PC World. Follow Ryan on Twitter @ryanaraine.
Hackers are exploiting a server vulnerability with a severity of 9.8 out of 10
Getty Images
In a development security pros feared, attackers are actively targeting yet another set of critical server vulnerabilities that leave corporations and governments open to serious network intrusions.
The vulnerability this time is in BIG-IP, a line of server appliances sold by Seattle-based F5 Networks. Customers use BIG-IP servers to manage traffic going into and out of large networks. Tasks include load balancing, DDoS mitigation, and web application security.
When security researchers weren’t busy attending to the unfolding Exchange mass compromise, many of them warned that it was only a matter of time before the F5 vulnerabilities also came under attack. Now, that day has come.
Researchers at security firm NCC Group on Friday said they’re “seeing full chain exploitation” of CVE-2021-22986, a vulnerability that allows remote attackers with no password or other credentials to execute commands of their choice on vulnerable BIG-IP devices.
“After seeing lots of broken exploits and failed attempts, we are now seeing successful in the wild exploitation of this vulnerability, as of this morning,” Rich Warren, Principal Security Consultant at NCC Group and co-author of the blog wrote.
After seeing lots of broken exploits and failed attempts, we are now seeing successful in the wild exploitation of this vulnerability, as of this morning https://t.co/Sqf55OFkzI
In a blog post NCC Group posted a screenshot showing exploit code that could successfully steal an authenticated session token, which is a type of browser cookie that allows administrators to use a web-based programming interface to remotely control BIG-IP hardware.
“The attackers are hitting multiple honeypots in different regions, suggesting that there is no specific targeting,” Warren wrote in an email. “It is more likely that they are ‘spraying’ attempts across the internet, in the hope that they can exploit the vulnerability before organizations have a chance to patch it.”
He said that earlier attempts used incomplete exploits that were derived from the limited information that was available publicly.
Security firm Palo Alto Networks, meanwhile, said that CVE-2021-22986 was being targeted by a devices infected with a variant of the open-source Mirai malware. The tweet said the variant was “attempting to exploit” the vulnerability, but it wasn’t clear if the attempts were successful.
Other researchers reported Internet-wide scans designed to locate BIG-IP servers that are vulnerable.
Opportunistic mass scanning activity detected from the following hosts checking for F5 iControl REST endpoints vulnerable to remote command execution (CVE-2021-22986).
CVE-2021-22986 is only one of several critical BIG-IP vulnerabilities F5 disclosed and patched last week. The severity In part is because the vulnerabilities require limited skill to exploit. But more importantly, once attackers have control of a BIG-IP server, they are more or less inside the security perimeter of the network using it. That means attackers can quickly access other sensitive parts of the network.
As if admins didn’t already have enough to attend to, patching vulnerable BIG-IP servers and looking for exploits should be a top priority. NCC Group provided indicators of compromise in the link above, and Palo Alto Networks has IOCs here.
Update: After this post went live, F5 issued a statement. It read: “We are aware of attacks targeting recent vulnerabilities published by F5. As with all critical vulnerabilities, we advise customers update their systems as soon as possible.”
Meanwhile, NCC Group’s Rich Warren responded to questions I sent earlier. Here’s a partial Q&A:
What does “seeing full chain exploitation” mean? What was NCC Group seeing before, and how does “full chain exploitation” change it?
What we mean is that, previously we were seeing attackers attempting to abuse the SSRF vulnerability in a way which could not work, because an important part of the exploit was not public knowledge, therefore the exploits would fail. Now, attackers have figured out the full details needed to use the SSRF to bypass authentication and obtain authentication tokens. These authentication tokens can then be used to execute commands remotely. So far, we have seen the attackers a) obtain an authentication token, and b) execute commands to dump credentials. We haven’t seen any web-shells being dropped like we did with CVE-2020-5902, yet.
Where, precisely, are you seeing the exploit attempts? Is it in a honeypot, on production servers, somewhere else?
The attackers are hitting multiple honeypots in different regions, suggesting that there is no specific targeting. It is more likely that they are “spraying” attempts across the internet, in the hope that they can exploit the vulnerability before organizations have a chance to patch it. Earlier attempts we saw against our honeypot infrastructure showed that attackers were using incomplete exploits based on limited information that was available in the public domain. This shows that attackers are obviously keen to exploit the vulnerability – even if some of them don’t have the requisite knowledge to engineer their own attack code.
Do you know if the exploits are succeeding in compromising production servers? If yes, what are attackers doing post exploitation?
At the moment we can’t comment on whether the same attackers have been successful against other people’s servers. With regards to post-exploitation activities, we have only seen credential dumping so far.
I’m reading that multiple threat groups are exploiting the vulnerability. Do you know this to be true? If so, how many different threat actors are there?
We’ve not stated that there are multiple attackers. In fact, while we’ve seen multiple successful exploitation attempts from different IPs, all attempts have contained some specific hallmarks which are consistent with the other attempts, suggesting it’s likely the same underlying exploit.
https://arstechnica.com/?p=1751018
Microsoft Defender Antivirus Now Protects Users Against Ongoing Exchange Attacks
Microsoft informed customers on Thursday that Defender Antivirus and System Center Endpoint Protection now provide automatic protection against attacks exploiting the recently disclosed Exchange Server vulnerabilities.
Microsoft has released patches, detailed guidance, and a one-click mitigation tool to ensure that Exchange Server users are protected against attacks. The tech giant has now taken another step to protect customers who haven’t managed to install the available patches but who have Defender deployed on vulnerable servers.
The Exchange vulnerabilities are tracked as CVE-2021-26855, CVE-2021-26857, CVE-2021-26858 and CVE-2021-27065, and they are tracked as ProxyLogon. They can be exploited by an unauthenticated attacker to execute arbitrary code on targeted servers and gain access to emails and other sensitive information.
When Microsoft disclosed the flaws and announced patches in early March, it warned that a threat actor linked to China had been exploiting them in attacks. Roughly one week after disclosure, others reported that several cyberspy and cybercrime groups had started exploiting the vulnerabilities.
As threat actors increasingly start to target these vulnerabilities, Microsoft has now decided to release a security intelligence update for Defender Antivirus and System Center Endpoint Protection (build 1.333.747.0 or newer), which according to the company “breaks the attack chain by mitigating CVE-2021-26855,” the first vulnerability exploited in the ProxyLogon chain.
Microsoft described this as an “interim mitigation” that should help customers protect their systems until they can install the patches.
“Microsoft Defender Antivirus will automatically identify if a vulnerable version of Exchange Server is installed and apply the mitigations the first time the security intelligence update is deployed. The mitigation is deployed once per machine,” Microsoft explained.
Eduard Kovacs (@EduardKovacs) is a contributing editor at SecurityWeek. He worked as a high school IT teacher for two years before starting a career in journalism as Softpedia’s security news reporter. Eduard holds a bachelor’s degree in industrial informatics and a master’s degree in computer techniques applied in electrical engineering.
Facebook Paid Out $50K for Vulnerabilities Allowing Access to Internal Systems
A researcher says he has earned more than $50,000 from Facebook after discovering vulnerabilities that could have been exploited to gain access to some of the social media giant’s internal systems.
Cybersecurity engineer and bug bounty hunter Alaa Abdulridha revealed in December 2020 that he had earned $7,500 from Facebook for discovering a vulnerability in a service apparently used by the company’s legal department. The researcher said the security hole could have been exploited to reset the password of any account for a web application used internally by Facebook employees.
In a blog post published on Thursday, the researcher said he continued analyzing the same application and once again managed to gain access to it. From there he claimed he was able to launch a server-side request forgery (SSRF) attack and gain access to Facebook’s internal network. Facebook described this as an attacker being able to send HTTP requests to internal systems and read their responses.
“I was able to scan the ports of the local servers and browse the local applications/web apps that the company uses in their infrastructure,” the researcher told SecurityWeek. “I’m sure such a vulnerability in the wrong hands could be escalated to RCE and can pose a huge risk for the company and its customers.”
The social media giant awarded him nearly $50,000 for this second exploit chain.
Abdulridha also claimed the account takeover attack may have allowed a hacker to access accounts for other internal Facebook applications as well, but Facebook told SecurityWeek it had not found any evidence to suggest that the flaw could be escalated to access other internal accounts.
Facebook has clarified that the vulnerabilities reported by Abdulridha actually affected a third-party service designed for signing documents and they impacted anyone using this service, not just Facebook. The company said it worked with the third-party vendor to quickly get the flaws fixed and said it had found no evidence of malicious exploitation, noting that exploiting the weaknesses was a complex task.
The company also pointed out that the first vulnerability only allowed access to accounts within the third-party document signing app, but did not grant access to any employee accounts used for other internal applications.
While the researcher claimed that it took Facebook nearly 6 months to patch the second round of vulnerabilities, the company told SecurityWeek that while the report was only closed in February, the bugs were actually completely fixed — by both Facebook and the third-party vendor — within a few days.
Facebook also said that while it paid out a bug bounty based on the maximum possible impact it could determine, it did not agree with the researcher’s belief that the SSRF vulnerabilities could have been escalated to remote code execution.
Eduard Kovacs (@EduardKovacs) is a contributing editor at SecurityWeek. He worked as a high school IT teacher for two years before starting a career in journalism as Softpedia’s security news reporter. Eduard holds a bachelor’s degree in industrial informatics and a master’s degree in computer techniques applied in electrical engineering.
Here’s How Security Flaws in GE Relays Could Be Exploited in Real World Attacks
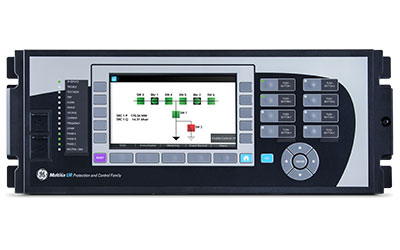
Organizations using Universal Relay (UR) products made by GE’s Grid Solutions have been informed this week that many of the devices in this product line are affected by nearly a dozen vulnerabilities.
Grid Solutions is a GE Renewable Energy business that provides electricity management solutions for the energy sector, including oil and gas, as well as industry and infrastructure organizations.
Advisories published this week by the U.S. Cybersecurity and Infrastructure Security Agency (CISA) and GE Grid Solutions (account required) inform customers that more than a dozen UR protection and control relays are impacted by a series of vulnerabilities to which 10 different CVE identifiers have been assigned. The vendor has released firmware updates that should patch the vulnerabilities.
The flaws are related to inadequate encryption of communications, exposure of potentially sensitive information, cross-site scripting (XSS) attacks, denial-of-service (DoS) attacks, unauthorized firmware uploading, the inability to disable a factory service mode, and the presence of hardcoded credentials in the bootloader. More than half of the vulnerabilities have a severity rating of high or critical.
Researchers from SCADA-X, Verve Industrial, VuMetric and the Department of Energy’s Cyber Testing for Resilient Industrial Control Systems (CyTRICS) program have been credited for finding the security holes.
Ron Brash, director of cyber security insights at ICS management and cybersecurity provider Verve Industrial Protection, told SecurityWeek that he has identified two or possibly three of the vulnerabilities — he says it’s difficult to say exactly due to multiple disclosures and some likely overlap. These include flaws that can be exploited to upload malicious firmware to the device, obtain potentially sensitive information, and access a device or disrupt it.
According to Brash, exploitation of these vulnerabilities requires direct or network access to the targeted system.
“Generally these devices are not found on the Internet directly unless someone has not applied any secure deployment strategies, or has inadvertently misconfigured various network infrastructure devices/security apparatuses,” he explained.
In terms of impact, the expert pointed out that while the vulnerable relays are used within the energy industry, they are not limited to the “grid.”
“For example, a mine may be generating power, and these types of devices might be present,” Brash explained. “This can mean that the results or motivations of what ‘an attacker could do’ might be situationally dependent, or require specific contexts. Therefore, in continuation of the example, if your mine needs energy to keep liquids unfrozen (e.g., washes, effluent management systems, etc), and the mine is located in Canada’s North, then you might have a BIG problem during winter. Secondly, if you can get access to these devices, and upload your own logic or firmware, then you can effectively brick them, upload malicious functionality, and the consequences will be highly negative.”
He added, “I don’t wish to speculate as to the motives, or what could be accomplished by an attacker, but if exploited at scale (which by the way, takes a great level of skill, budget, and organization) – nothing positive would result.”
Contacted by SecurityWeek, GE said it’s currently not aware of any attacks exploiting these vulnerabilities.
“GE was made aware of vulnerabilities related to GE’s Grid Solutions’ Universal Relay (UR) family products and immediately worked to assess any potential impact and remediate the reported vulnerabilities. GE’s UR firmware Version 8.10 and greater resolve the identified vulnerabilities, and we encourage our customers to visit the Grid Solutions customer portal and/or the CISA Advisory for additional information and mitigation recommendations,” said a GE spokesperson.
Eduard Kovacs (@EduardKovacs) is a contributing editor at SecurityWeek. He worked as a high school IT teacher for two years before starting a career in journalism as Softpedia’s security news reporter. Eduard holds a bachelor’s degree in industrial informatics and a master’s degree in computer techniques applied in electrical engineering.
“Expert” hackers used 11 zerodays to infect Windows, iOS, and Android users
A team of advanced hackers exploited no fewer than 11 zeroday vulnerabilities in a nine-month campaign that used compromised websites to infect fully patched devices running Windows, iOS, and Android, a Google researcher said.
Using novel exploitation and obfuscation techniques, a mastery of a wide range of vulnerability types, and a complex delivery infrastructure, the group exploited four zerodays in February 2020. The hackers’ ability to chain together multiple exploits that compromised fully patched Windows and Android devices led members of Google’s Project Zero and Threat Analysis Group to call the group “highly sophisticated.”
Not over yet
On Thursday, Project Zero researcher Maddie Stone said that, in the eight months that followed the February attacks, the same group exploited seven more previously unknown vulnerabilities, which this time also resided in iOS. As was the case in February, the hackers delivered the exploits through watering-hole attacks, which compromise websites frequented by targets of interest and add code that installs malware on visitors’ devices.
In all the attacks, the watering-hole sites redirected visitors to a sprawling infrastructure that installed different exploits depending on the devices and browsers visitors were using. Whereas the two servers used in February exploited only Windows and Android devices, the later attacks also exploited devices running iOS. Below is a diagram of how it worked:
The ability to pierce advanced defenses built into well-fortified OSes and apps that were fully patched—for example, Chrome running on Windows 10 and Safari running on iOSA—was one testament to the group’s skill. Another testament was the group’s abundance of zerodays. After Google patched a code-execution vulnerability the attackers had been exploiting in the Chrome renderer in February, the hackers quickly added a new code-execution exploit for the Chrome V8 engine.
The vulnerabilities cover a fairly broad spectrum of issues—from a modern JIT vulnerability to a large cache of font bugs. Overall each of the exploits themselves showed an expert understanding of exploit development and the vulnerability being exploited. In the case of the Chrome Freetype 0-day, the exploitation method was novel to Project Zero. The process to figure out how to trigger the iOS kernel privilege vulnerability would have been non-trivial. The obfuscation methods were varied and time-consuming to figure out.
In all, Google researchers gathered:
1 full chain targeting fully patched Windows 10 using Google Chrome
2 partial chains targeting 2 different fully patched Android devices running Android 10 using Google Chrome and Samsung Browser, and
RCE exploits for iOS 11-13 and privilege escalation exploit for iOS 13
CVE-2020-27932 – iOS kernel type confusion with turnstiles
Piercing defenses
The complex chain of exploits is required to break through layers of defenses that are built into modern OSes and apps. Typically, the series of exploits are needed to exploit code on a targeted device, have that code break out of a browser security sandbox, and elevate privileges so the code can access sensitive parts of the OS.
Thursday’s post offered no details on the group responsible for the attacks. It would be especially interesting to know if the hackers are part of a group that’s already known to researchers or if it’s a previously unseen team. Also useful would be information about the people who were targeted.
The importance of keeping apps and OSes up to date and avoiding suspicious websites still stands. Unfortunately, neither of those things would have helped the victims hacked by this unknown group.
https://arstechnica.com/?p=1750760
Facebook Now Lets Mobile Users Secure Accounts with Security Keys
Social media and advertising giant Facebook today announced that it is now allowing mobile users to secure their accounts with the help of security keys.
Available for Facebook’s desktop users since 2017, the authentication method requires that the user confirm authentication requests with the help of a physical security key.
This additional authentication step is meant to significantly increase account protection, as it relies on the use of a physical device that an attacker is assumed to never have access to.
“Starting today, you can set up two-factor authentication and log into Facebook on iOS and Android mobile devices using a security key, available to anyone in the world,” Facebook announced.
Two-factor authentication (2FA) has evolved from codes sent via SMS or email to the use of authenticator applications and security keys, making it increasingly difficult for a threat actor to come in the possession of both the account password and the second factor.
Since 2017, Facebook has been providing users the option to enable 2FA and choose physical security keys as the second authentication factor, with that feature now available for iOS and Android users as well.
Users who may need such strong authentication protection are those most exposed to malicious attacks, including public figures, politicians, journalists, and human rights defenders, among others.
“We strongly recommend that everyone considers using physical security keys to increase the security of their accounts, no matter what device you use,” Facebook says.
Security keys can be connected either via Bluetooth or can be directly plugged into phones.
To enable the use of security keys as the authentication method, Facebook users should head over to the Security and Login section of the Settings menu.
The social platform also says it plans to expand the availability of its Facebook Protect program to include additional at-risk groups, alongside political campaigns and candidates.


 Tags:
 Researchers at industrial cybersecurity firm Claroty discovered last year that the TBox RTUs, as well as the associated TWinSoft engineering software, are affected by five types of vulnerabilities.


 Tags:


 Tags:


 Tags:


 Tags:
 The flaws are related to inadequate encryption of communications, exposure of potentially sensitive information, cross-site scripting (XSS) attacks, denial-of-service (DoS) attacks, unauthorized firmware uploading, the inability to disable a factory service mode, and the presence of hardcoded credentials in the bootloader. More than half of the vulnerabilities have a severity rating of high or critical.


 Tags:


 Tags: