Healthcare IoT Security Firm Cylera Closes $10 Million Series A Round

Healthcare IoT cybersecurity and intelligence provider Cylera today announced that it has raised $10 million in Series A funding. To date, the company has secured $17 million in funding.

Founded in 2017 and headquartered in New York City, Cylera seeks to protect both healthcare organizations and patients, providing a security and analytics platform that aims to deliver asset management, risk analysis, and threat detection for IoT, ICS, and IoMT (Internet of Medical Things).

Cylera seeks to secure the entire connected environment, providing insights and recommendations that simplify response, accelerate remediation, and improve the decision making process.

Cylera’s Series A funding round was led by Concord Health Partners and Maverick Ventures. Previous investors include Dreamit Ventures, Great Oaks Venture Capital, Red Bear Angels, and Samsung NEXT.

The funds will help the company expand to new global markets, as well as make its technology available for new verticals. Furthermore, Cylera plans to expand its research and development, customer success, channel support, and sales and marketing teams.

“Over the past year there has been a further acceleration of the digitalization and adoption of IoT devices across hospitals, pharmaceutical companies, biotech, life sciences and manufacturing in an effort to decrease operational risk and increase efficiencies. […] With our latest round of funding, Cylera is fueling the next phase of innovation to safeguard organizations against attacks on connected devices,” Cylera co-founder and CEO Timur Ozekcin said.

Related: HD Moore Banks $5M Funding for Rumble Asset Management

Related: Aqua Security Hits Unicorn Status After $135 Million Funding Round

Related: Cyber Insurance Company Coalition Raises $175 Million

view counter

Ionut Arghire is an international correspondent for SecurityWeek.

Previous Columns by Ionut Arghire:
Tags:

http://feedproxy.google.com/~r/Securityweek/~3/a5KE8ovM3a0/healthcare-iot-security-firm-cylera-closes-10-million-series-round


Chinese Cyberspies Target Telecom Companies in America, Asia, Europe

China-linked cyber-espionage group Mustang Panda is targeting telecommunications companies in Asia, Europe, and the United States for espionage purposes, according to a warning from security researchers at McAfee.

Also referred to as RedDelta and TA416, the threat actor has been previously associated with the targeting of entities in connection with the Vatican – Chinese Communist Party diplomatic relations, along with some entities in Myanmar.

The new malware attacks, McAfee says, employ the same tactics, techniques and procedures (TTPs) previously associated with Mustang Panda. The initial vector of infection hasn’t been identified, but the researchers believe that victims were being lured to a fake website crafted to mimic the legitimate career site for Chinese tech giant Huawei.

The first stage of the attack leverages a fake Flash application and a phishing page mimicking the original website, while the second stage is a .Net payload executed to further compromise the machine through downloading and managing backdoors. A Cobalt Strike beacon payload is delivered as a third stage.

Referred collectively as Operation Diànxùn, the new attacks were targeted at telecommunication companies in based in Southeast Asia, Europe, and the United States. The adversary, McAfee says, shows strong interest in German, Vietnamese, and Indian telecommunication companies.

“Combined with the use of the fake Huawei site, we believe with a high level of confidence that this campaign was targeting the telecommunication sector. We believe with a moderate level of confidence that the motivation behind this specific campaign has to do with the ban of Chinese technology in the global 5G roll-out,” McAfee says.

The campaign, the researchers note, is believed to have been aimed at the theft of sensitive or secret information related to 5G technology. McAfee also notes that it has no evidence that Huawei was knowingly involved in these attacks.

Related: China-Linked Hackers Exploited SolarWinds Flaw in U.S. Government Attack: Report

Related: Facebook Says Fake Accounts From China Aimed at US Politics

view counter

Ionut Arghire is an international correspondent for SecurityWeek.

Previous Columns by Ionut Arghire:
Tags:

http://feedproxy.google.com/~r/Securityweek/~3/L5Vth0BDCV0/chinese-cyberspies-target-telecom-companies-america-asia-europe


HD Moore Banks $5M Funding for Rumble Asset Management Startup

Network and asset discovery provider Rumble this week announced that it has raised $5 million in VC funding. The round was led by Jon Sakoda and Dan Nguyen-Huu at Cisco-backed Decibel Partners.

The round also saw participation from Duo Security co-founder and CTO Jon Oberheide, Demisto (acquired by Palo Alto Networks) founders Slavik Markovich and Rishi Bhargava, Phantom  Cyber (acquired by Splunk) founder and CEO Oliver Friedrichs, Thinkst Canary founder Haroon Meer, and StoneMill Ventures founder Michael Sutton.

Founded by H.D. Moore, who is best known for creating Metasploit and who also started Rapid7’s Project Sonar, Rumble officially launched in October 2019, after a six-month beta period. At the end of 2020, the company had over 100 paying customers.

The Rumble platform has been designed to inventory inventories IT and OT environments to help with attack surface reduction and incident response.

Rumble’s Explorer scanner was designed to identify outdated and orphaned devices and rogue RDP ports, as well as for the discovery of public-private network bridges, thus increasing security teams’ visibility into enterprise environments.

The new funds, Rumble says, will help it expand the enterprise capabilities of its platform and also accelerate its go-to-market engine.

The funding round was accompanied by Rumble’s 2.0 release, which features ServiceNow ITOM CMDB integration, new discovery modes to identify active subnets and hosts, automated monitoring, expanded API capabilities, and more.

“Most security teams have been trying to get asset inventory data from solutions that weren’t designed for it, such as vulnerability scanners and EDR agents. These solutions weren’t created with that goal in mind, so the data is often spotty, either because it doesn’t properly identify the device or misses it altogether,” HD Moore commented.

Related: Authentication Provider LoginID Raises $6 Million in Seed Funding

Related: 1Kosmos Emerges from Stealth Mode With $15 Million in Funding

Related: Data Privacy Startup TripleBlind Raises $8.2 Million in Seed Funding

view counter

Ionut Arghire is an international correspondent for SecurityWeek.

Previous Columns by Ionut Arghire:
Tags:

http://feedproxy.google.com/~r/Securityweek/~3/wSgUbfqQkx8/hd-moore-banks-5m-funding-rumble-asset-management-startup


Recorded Future Buys Fraud Analytics Startup Gemini Advisory

Threat Intelligence Firm Recorded Future Buys Company Started by Former Employee in $52 Million Deal

Threat intelligence data broker Recorded Future has acquired fraud analytics startup Gemini Advisory as part of a strategic push to expand into the financial services and payment processing markets.

The cash and stock deal is valued at $52 million and comes less than a year after Recorded Future was itself acquired in a $780 million transaction.

Recorded Future expects the Gemini Advisory deal to provide tools and expertise to sell the “most comprehensive intelligence platform” with “the visibility to act at the speed of the adversary to mitigate cyber risk and fraud.”

Upon acquisition, Gemini Advisory will operate as an independent business unit inside of Recorded Future.   

Gemini Advisory is the brainchild of former FBI consultant Andrei Barysevi, who left Recorded Future three years ago to create the new company. 

“In a short time, Gemini Advisory has become a leader in the fraud space with unique offerings in both payment card intelligence and merchant fraud intelligence,” said Recorded Future CEO Christopher Ahlberg. 

“As we continue to execute on our mission to deliver a modular intelligence platform, joining forces with Gemini Advisory expands the value we deliver for customers across enterprise security and fraud,” he added.

Recorded Future itself was acquired by private equity firm Insight Partners for $780 million in a cash deal announced in May 2019.

Related: Recorded Future Acquired for $780M

Related: Recorded Future Adds Third-Party Risk to Threat Intel Platform

view counter

Previous Columns by SecurityWeek News:
Tags:

http://feedproxy.google.com/~r/Securityweek/~3/F1Dvt4680Jo/recorded-future-buys-fraud-analytics-startup-gemini-advisory


Over 80,000 Exchange Servers Still Affected by Actively Exploited Vulnerabilities

Roughly 80,000 Exchange servers have yet to receive patches for the actively exploited vulnerabilities, Microsoft says.

The bugs were publicly disclosed on March 2, when the Redmond-based tech giant announced not only patches for them, but also the fact that a Chinese threat actor had been actively exploiting them in attacks.

Within days, security researchers revealed that multiple adversaries were quick to pick up exploits for the Exchange bugs, but also that some had been targeting the flaws even before patches were released. The first known exploitation attempt is dated January 3, 58 days before public disclosure.

Over the course of last week, Microsoft released additional fixes for these vulnerabilities, including security updates (SUs) for older and unsupported Exchange Server versions, or Cumulative Updates (CU), as the company calls them.

“This is intended only as a temporary measure to help you protect vulnerable machines right now. You still need to update to the latest supported CU and then apply the applicable SUs,” Microsoft said.

With the latest set of released updates, more than 95% of the Exchange Server versions that are exposed to the Internet are covered, yet tens of thousands of machines remain vulnerable. Microsoft revealed that, as of March 12, more than 82,000 Exchange servers were still left to be updated (out of 400,000 identified on March 1).

Last week, ESET reported that more than 10 threat actors were observed targeting vulnerable Exchange servers. Ransomware operators also started targeting the flaws, and the overall number of attacks aimed at the Exchange zero-days grew exponentially over the course of several days only.

On Sunday, security researchers at Check Point pointed out that “the number exploitation attempts multiplied by more than 6 times” within “the past 72 hours alone,” adding that they had identified more than 4,800 exploits and hundreds of compromised organizations worldwide.

The United States was being targeted the most, accounting for 21% of all exploitation attempts, followed by the Netherlands and Turkey, both at 12%. According to Check Point, government/military was the sector being targeted the most (27% of attempts), followed by manufacturing (22%) and software (9%).

“As we enter the second week since the vulnerabilities became public, initial estimates place the number of compromised organizations in the tens of thousands,” Palo Alto Networks said last week.

In a timeline of the attacks, the security firm revealed that the first two bugs were identified on December 10 and 30, 2020, respectively, and reported to Microsoft on January 5, 2021. A third security hole was identified and reported while already under attack, on January 27.

“Ongoing research illustrates that these vulnerabilities are being used by multiple threat groups. While it is not new for highly skilled attackers to leverage new vulnerabilities across varying product ecosystems, the ways in which these attacks are conducted to bypass authentication — thereby providing unauthorized access to emails and enabling remote code execution (RCE) — is particularly nefarious,” Palo Alto Networks noted.

Microsoft published additional information on how organizations can protect their on-premises Exchange servers against exploitation, reiterating that applying the available patches represents the first step, followed by identifying possibly compromised systems and removing them from the network.

Related: Microsoft Shares Additional Mitigations for Exchange Server Vulnerabilities Under Attack

view counter

Ionut Arghire is an international correspondent for SecurityWeek.

Previous Columns by Ionut Arghire:
Tags:

http://feedproxy.google.com/~r/Securityweek/~3/xeA6hzA1QKM/over-80000-exchange-servers-still-affected-actively-exploited-vulnerabilities


Google Chrome Zero-Day Under Attack, Again

For the third time this year, Google has shipped an urgent fix to block in-the-wild zero-day attacks hitting its flagship Chrome browser.

The latest emergency Chrome patch, available for Windows, MacOS and Linux, provides cover for at least five (5) documented vulnerabilities. Three of the five bugs are rated “high-risk,” Google’s highest severity rating.

Buried in Google’s advisory is a throwaway line that “Google is aware of reports that an exploit for CVE-2021-21193 exists in the wild.”

The company did not release any additional information on the live attacks or the operating system platforms being targeted.  

It is the third in-the-wild zero-day attack hitting Chrome users in 2021, and in all three cases, Google has been stingy with information on the malware used, the OS platforms targeted or the indicators of compromise that help enterprise defenders.  

In one prominent case, the North Korean state-sponsored hacks against security researchers, Google has barely confirmed the existence of the Chrome zero-day with a one-line mentioned that fully-patched Chrome installations were being compromised. 

The latest zero-day is described simply as a use-after-free vulnerability in Chrome’s Blink rendering engine that was anonymously reported to Google.

By contrast, when Google research teams discovered a massive cyber-espionage operation rampant on Apple’s iOS platform, the company produced a riveting blog post with “a very deep dive into iOS Exploit chains found in the wild.”

The Chrome patch is being pushed to Chrome users via the browser’s automatic updating mechanism but users are urged to restart browser sessions to properly apply the fixes.

Related: Google Chrome, Microsoft IE Zero-Days in Crosshairs

Related: Google Warns of North Korean Gov Hackers Targeting Security Researchers

view counter

Ryan Naraine is Editor-at-Large at SecurityWeek and host of the popular Security Conversations podcast series. Ryan is a journalist and cybersecurity strategist with more than 20 years experience covering IT security and technology trends. He is a regular speaker at cybersecurity conferences around the world.
Ryan has built security engagement programs at major global brands, including Intel Corp., Bishop Fox and Kaspersky GReAT. He is a co-founder of Threatpost and the global SAS conference series. Ryan’s career as a journalist includes bylines at major technology publications including Ziff Davis eWEEK, CBS Interactive’s ZDNet, PCMag and PC World.
Follow Ryan on Twitter @ryanaraine.

Previous Columns by Ryan Naraine:
Tags:

http://feedproxy.google.com/~r/Securityweek/~3/dQMekthiDUo/google-chrome-zero-day-under-attack-again


Google Releases PoC Exploit for Browser-Based Spectre Attack

Google last week announced the release of proof-of-concept (PoC) code designed to exploit the notorious Spectre vulnerability and leak information from web browsers.

Initially detailed in early 2018 alongside Meltdown, the side-channel attack could allow a malicious application to access data being processed on the device. The vulnerability could expose passwords, documents, emails, data from instant messaging apps, and more.

Since the public disclosure of Meltdown and Spectre, both hardware makers and software developers alike have been working on devising protections against similar flaws, and browser makers too have been implementing application-level mitigations.

In 2019, the Google team responsible for Chrome’s V8 JavaScript engine said that the attack can’t be mitigated at the software level, arguing that security boundaries in browsers should be aligned with low-level primitives, such as process-based isolation.

To keep their users safe, browser makers have already implemented protections such as Site Isolation, Cross-Origin Read Blocking, and out-of-process iframes, with a variety of security features available for other application developers as well, including Cross-Origin Resource and Cross-Origin Opener Policies, and more.

The purpose of these mechanisms is to prevent sensitive data from being present in memory sections that an attacker could read. However, they do not prevent Spectre exploitation.

In order to assess the effectiveness of such mitigations, Google’s researchers have released JavaScript PoC code functional across multiple operating systems, architectures, and hardware variants, and which “confirms the practicality of Spectre exploits against JavaScript engines.”

While Chrome has been used to demonstrate the attack, the exploited issues are not specific to Google’s browser, but affect other modern browsers as well. An interactive demonstration of the attack can be accessed on this page, while the code and technical details were published on Github.

“The demonstration website can leak data at a speed of 1kB/s when running on Chrome 88 on an Intel Skylake CPU. Note that the code will likely require minor modifications to apply to other CPUs or browser versions; however, in our tests the attack was successful on several other processors, including the Apple M1 ARM CPU, without any major changes,” Google explains.

In addition to releasing the PoC, Google is making recommendations (Post-Spectre Web Development and Mitigating Side-Channel Attacks) on how web developers can improve site isolation to deny access to cross-origin resources, thus effectively mitigating Spectre-style hardware attacks, among others.

Such mitigations include Cross-Origin Resource Policy (CORP) and Fetch Metadata Request Headers, Cross-Origin Opener Policy (COOP), and Cross-Origin Embedder Policy (COEP), along with standard protections, such as the X-Frame-Options and X-Content-Type-Options headers, along with SameSite cookies.

“It’s important to note that while […] the mechanisms […] are important and powerful security primitives, they don’t guarantee complete protection against Spectre; they require a considered deployment approach which takes behaviors specific to the given application into account,” Google notes.

Related: Microsoft Brings Hardware-Based Isolation to Chrome, Firefox

Related: Should You Be Concerned About the Recently Leaked Spectre Exploits?

view counter

Ionut Arghire is an international correspondent for SecurityWeek.

Previous Columns by Ionut Arghire:
Tags:

http://feedproxy.google.com/~r/Securityweek/~3/fRZF95Bg-ZQ/google-releases-poc-exploit-browser-based-spectre-attack


WSJ: Microsoft Probing Possible PoC Exploit Code Leak

Software giant Microsoft Corp. has launched an investigation to determine whether one of its flagship information-sharing programs sprung a leak that led to the widespread exploitation of Exchange server deployments around the world.

According to a bombshell report in the Wall Street Journal, Redmond is looking closely at its Microsoft Active Protections Program (MAPP) to figure out if an anti-malware partner in China leaked proof-of-concept code ahead of the availability of security updates.

The MAPP program lets Microsoft share vulnerability data to give anti-malware, intrusion prevention/detection and corporate network security vendors a head-start to add signatures and filters to protect against Microsoft software vulnerabilities. 

The program is popular with defenders but it has long been controversial because of there is legitimate risk that data on serious, unpatched vulnerabilities could land in the wrong hands.

[ ALSO SEE: Microsoft Drops Chinese Vendor From MAPP  ]

In 2012, Microsoft dropped a Chinese vendor from the program after violations and there is rampant speculation that something similar happened in late February this year ahead of the Exchange Server patches.

The WSJ says Microsoft’s new investigation centers on the question of how a stealthy attack that began in early January picked up steam in the week before the company was able to send a software fix to customers. 

From the WSJ article:

Some of the tools used in the second wave of the attack, which is believed to have begun Feb. 28, bear similarities to “proof-of-concept” attack code that Microsoft distributed to antivirus companies and other security partners Feb. 23, investigators at security companies say. Microsoft had planned to release its security fixes two weeks later, on March 9, but after the second wave began it pushed out the patches a week early, on March 2, according to researchers.

One focus of the investigation has been an information-sharing program called the Microsoft Active Protections Program, which was created in 2008 to give security companies a head start in detecting emerging threats. Mapp includes about 80 security companies world-wide, about 10 of which are based in China. A subset of the Mapp partners were sent the Feb. 23 Microsoft notification, which included the proof-of-concept code, according to sources familiar with the program. 

The report said Microsoft declined to say whether any Chinese companies were included in this release.

Microsoft’s probe comes amidst news that ransomware gangs are starting to take aim at the Exchange Server vulnerabilities, adding a new sense of urgency to the need for organization to apply patches and disinfect backdoors from networks.

Related: Microsoft Shares Additional Exchange Server Mitigations 

Related: Microsoft to Share Vulnerability Data with Incident Responders

Related: Microsoft Drops Chinese Vendor From MAPP After NDA Violations

view counter

Ryan Naraine is Editor-at-Large at SecurityWeek and host of the popular Security Conversations podcast series. Ryan is a journalist and cybersecurity strategist with more than 20 years experience covering IT security and technology trends. He is a regular speaker at cybersecurity conferences around the world.
Ryan has built security engagement programs at major global brands, including Intel Corp., Bishop Fox and Kaspersky GReAT. He is a co-founder of Threatpost and the global SAS conference series. Ryan’s career as a journalist includes bylines at major technology publications including Ziff Davis eWEEK, CBS Interactive’s ZDNet, PCMag and PC World.
Follow Ryan on Twitter @ryanaraine.

Previous Columns by Ryan Naraine:
Tags:

http://feedproxy.google.com/~r/Securityweek/~3/xpMh1Fe8qkQ/wsj-microsoft-probing-possible-poc-exploit-code-leak


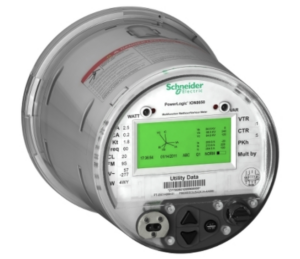
Serious Vulnerabilities Found in Schneider Electric Power Meters

Industrial cybersecurity firm Claroty this week disclosed technical details for two potentially serious vulnerabilities affecting PowerLogic smart meters made by Schneider Electric.

PowerLogic is a line of revenue and power quality meters that are used not only by utilities, but also industrial companies, healthcare organizations, and data centers for monitoring electrical networks.

Researchers at Claroty discovered that some of the PowerLogic ION and PM series smart meters are affected by vulnerabilities that can be exploited remotely by an unauthenticated attacker by sending specially crafted TCP packets to the targeted device.

Vulnerabilities found in Schneider Electric PowerLogic power meters“These smart meters communicate using a proprietary ION protocol over TCP port 7700, and packets received by the device are parsed by a state machine function,” Claroty explained in a blog post. “We found that It is possible to trigger the flaw during the packet-parsing process by the main state machine function by sending a crafted request. This can be done without authentication because the request is fully parsed before it is handled or authentication is checked.”

Claroty said its researchers identified two different exploitation paths — depending on the architecture of the targeted device — and two different CVE identifiers have been assigned.

One of them, CVE-2021-22714, is considered critical as it allows an attacker to cause the targeted meter to reboot (i.e. DoS condition) and possibly even to execute arbitrary code. The other one, CVE-2021-22713, can only be exploited to force the device to reboot and it has been assigned a high severity rating.

Learn more about vulnerabilities in industrial systems at SecurityWeek’s ICS Cyber Security Conference and SecurityWeek’s Security Summits virtual event series

The vulnerabilities impact several PowerLogic ION device models and one PM model. Security updates for some of the impacted devices were released in July 2020, while others were patched in January and March 2021. Some of the impacted power meters will not receive patches as they are no longer supported.

Vulnerabilities affecting smart meters have been known to pose a risk to both consumers and utilities so it’s important that users of the affected Schneider Electric products apply the patches or mitigations to prevent potential attacks, particularly since information about the flaws has been made public.

Additional details about the patches and mitigations are available in the advisories (CVE-2021-22714 and CVE-2021-22713) released this week by Schneider Electric.

Related: Several Vulnerabilities Found in GE Power Meter Software

Related: Siemens Says Power Meters Affected by Urgent/11 Vulnerabilities

Related: ICS-CERT Issues Alerts After Expert Discloses Power Meter Flaws

view counter

Eduard Kovacs (@EduardKovacs) is a contributing editor at SecurityWeek. He worked as a high school IT teacher for two years before starting a career in journalism as Softpedia’s security news reporter. Eduard holds a bachelor’s degree in industrial informatics and a master’s degree in computer techniques applied in electrical engineering.

Previous Columns by Eduard Kovacs:
Tags:

http://feedproxy.google.com/~r/Securityweek/~3/PJ8CycY3iQc/serious-vulnerabilities-found-schneider-electric-power-meters


Tausight Raises $20M to Protect Healthcare Data

Patient data protection provider Tausight this week announced that it has raised $20 million in Series A funding.

The new funding, Tausight says, will help expand the go-to-market team and invest in a healthcare-specific solution designed to identify security flaws in clinical workflows.

The new funding round was co-led by existing investors Polaris Partners and Flare Capital Partners. New investor .406 Ventures also participated.

Founded in 2018 and based in Boston, Mass., Tausight aims to help organizations ensure the confidentiality, integrity, and availability of patients’ protected health information (PHI).

Tausight’s offerings help healthcare provider CIOs, CISOs, and IT organizations understand the risk associated with the manner in which PHI is used, and help them secure access to clinical workflows and PHI.

“Existing cybersecurity solutions address critical aspects of securing the healthcare IT system but are not adequately addressing hidden vulnerabilities found in clinical workflows – Tausight was created to close this gap and solve this vital problem,” Tausight CEO Dave Dickinson said.

Related: Snyk Raises $300 Million at $4.7 Billion Valuation

Related: Cyber Insurance Provider Corvus Raises $100 Million

Related: OwnBackup Achieves ‘Unicorn’ Status With $167.5M Funding

view counter

Ionut Arghire is an international correspondent for SecurityWeek.

Previous Columns by Ionut Arghire:
Tags:

http://feedproxy.google.com/~r/Securityweek/~3/gSsIrOndL-8/tausight-raises-20m-protect-healthcare-data