At Least 10 Threat Actors Targeting Recent Microsoft Exchange Vulnerabilities

At least 10 threat actors are currently involved in the targeting of Microsoft Exchange servers that are affected by recently disclosed zero-day vulnerabilities, according to cybersecurity firm ESET.

On March 2, Microsoft announced patches for four bugs (CVE-2021-26855, CVE-2021-26857, CVE-2021-26858, and CVE-2021-27065) that were part of a pre-authentication remote code execution (RCE) attack chain already being exploited in the wild.

Successful exploitation of the bugs could result in the attacker deploying webshells onto the vulnerable Exchange servers, potentially taking full control of them. To date, ESET has identified more than 5,000 compromised servers, but others previously reported that tens of thousands of organizations may have been hacked.

Last week, Microsoft said that the flaws were being exploited by Chinese hacking group HAFNIUM, but security researchers were quick to report that several cyber-espionage groups were already targeting the vulnerable Exchange servers.

Now, ESET reveals that at least 10 threat actors are actively engaged in such attacks, including Tick (also known as Bronze Butler), LuckyMouse (also tracked as APT27), Calypso, Websiic, Winnti Group (BARIUM, APT41), Tonto Team (CactusPete), ShadowPad, Mikroceen, and DLTMiner. Activity involving the “Opera” Cobalt Strike and IIS backdoors was also observed.

“On 2021-02-28, we noticed that the vulnerabilities were used by other threat actors, starting with Tick and quickly joined by LuckyMouse, Calypso and the Winnti Group. This suggests that multiple threat actors gained access to the details of the vulnerabilities before the release of the patch,” ESET notes.

Immediately after the patches were released, the researchers noticed a spike in attacks, with adversaries “scanning and compromising Exchange servers en masse.” Overall, more than 10 different threat actors are currently abusing the RCE exploit chain to install implants on vulnerable servers.

“Once the vulnerability had been exploited and the webshell was in place, we observed attempts to install additional malware through it. We also noticed in some cases that several threat actors were targeting the same organization,” ESET says.

Targeted organizations include governmental entities, IT services providers and other private companies (IT, telecommunications, engineering, oil, construction equipment, procurement, cybersecurity consulting, software development, and utility).

“Our ongoing research shows that […] multiple APTs have access to the exploit, and some even did so prior to the patch release. It is still unclear how the distribution of the exploit happened, but it is inevitable that more and more threat actors, including ransomware operators, will have access to it sooner or later,” ESET notes.

The targeted entities are located in the US, Germany, the UK and other European countries (including some located in Eastern Europe), Asia, South America, Africa, and the Middle East.

According to Reuters, at least “60,000 computer systems in Germany” were exposed to the Exchange zero-day flaws. Norway’s parliament, the Storting, was affected by these attacks as well. With proof-of-concept code published online, the number of attacks will only increase.

On Wednesday, the Federal Bureau of Investigation (FBI) and the Cybersecurity and Infrastructure Security Agency (CISA) issued a joint advisory on the compromise of Exchange servers, noting that both state-sponsored actors and cybercriminals are targeting the zero-day flaws.

The attacks could result in adversaries gaining access to and control of enterprise networks, the two agencies warn, adding that tens of thousands of systems in the United States — containing research, personally identifiable information (PII), technology data, and other sensitive information — are potentially at risk.

“Threat actors have targeted local governments, academic institutions, non-governmental organizations, and business entities in multiple industry sectors, including agriculture, biotechnology, aerospace, defense, legal services, power utilities, and pharmaceutical,” the advisory reads.

The FBI and CISA also note that threat actors will continue to exploit these issues, looking to compromise networks and exfiltrate data, encrypt data for ransom, sell access to the compromised networks, or even launch destructive attacks on the vulnerable systems.

Related: Microsoft Shares Additional Mitigations for Exchange Server Vulnerabilities Under Attack

view counter

Ionut Arghire is an international correspondent for SecurityWeek.

Previous Columns by Ionut Arghire:
Tags:

http://feedproxy.google.com/~r/Securityweek/~3/yIoyoBkw9sw/least-10-threat-actors-targeting-recent-microsoft-exchange-vulnerabilities


There’s a vexing mystery surrounding the 0-day attacks on Exchange servers

The phrase Zero Day can be spotted on a monochrome computer screen clogged with ones and zeros.

The Microsoft Exchange vulnerabilities that allow hackers to take over Microsoft Exchange servers are under attack by no fewer than 10 advanced hacking groups, six of which began exploiting them before Microsoft released a patch, researchers reported Wednesday. That raises a vexing question: how did so many separate threat actors have working exploits before the security flaws became publicly known?

Researchers say that as many as 100,000 mail servers around the world have been compromised, with those for the European Banking Authority and Norwegian Parliament being disclosed in the past few days. Once attackers gain the ability to execute code on the servers, they install web shells, which are browser-based windows that provide a means for remotely issuing commands and executing code.

When Microsoft issued emergency patches on March 2, the company said the vulnerabilities were being exploited in limited and targeted attacks by a state-backed hacking group in China known as Hafnium. On Wednesday, ESET provided a starkly different assessment. Of the 10 groups ESET products have recorded exploiting vulnerable servers, six of those APTs—short for advanced persistent threat actors—began hijacking servers while the critical vulnerabilities were still unknown to Microsoft.

It’s not often that a so-called zero-day vulnerability is exploited by two groups in unison, but it happens. A zero-day under attack by six APTs simultaneously, on the other hand, is highly unusual, if not unprecedented.

“Our ongoing research shows that not only Hafnium has been using the recent RCE vulnerability in Exchange, but that multiple APTs have access to the exploit, and some even did so prior to the patch release,” ESET researchers Matthieu Faou, Mathieu Tartare, and Thomas Dupuy wrote in a Wednesday post. “It is still unclear how the distribution of the exploit happened, but it is inevitable that more and more threat actors, including ransomware operators, will have access to it sooner or later.”

Beyond unlikely

The mystery is compounded by this: within a day of Microsoft issuing the patches, at least three more APTs joined the fray. A day later, another one was added to the mix. While it’s possible that those four groups reverse-engineered the fixes, developed weaponized exploits, and deployed them at scale, those types of activities usually take time. A 24-hour window is on the short side.

There’s no clear explanation for the mass exploitation by so many different groups, leaving researchers few alternatives other than to speculate.

“It would seem that while the exploits were originally used by Hafnium, something made them share the exploit with other groups around the time the associated vulnerabilities were getting patched by Microsoft,” Costin Raiu, director of the Global Research and Analysis Team at Kaspersky Lab, told me. “This could suggest a certain degree of cooperation between these groups, or it may also suggest the exploits were available for sale in certain markets and the potential of them getting patched resulted in a drop of price, allowing others to acquire it as well.”

Juan Andres Guerrero-Saade, principal threat researcher at security firm SentinelOne, arrived at largely the same assessment.

“The idea that six groups coming from the same region would independently discover the same chain of vulnerabilities and develop the same exploit is beyond unlikely,” he wrote in a direct message. “The simpler explanation is that there’s (a) an exploit seller in common, (b) an unknown source (like a forum) available to all of these, or (c) a common entity that organizes these different hacking groups and provided them the exploit to ease their activities (say, China’s Ministry of State Security).”

Naming names

The six groups ESET identified exploiting the vulnerabilities when they were still zero-days are:

  • Hafnium: The group, which Microsoft said is state sponsored and based in China, was exploiting the vulnerabilities by early January.
  • Tick (also known as Bronze Butler and RedBaldKnight): On February 28, two days before Microsoft issued patches, this group used the vulnerabilities to compromise the web server of an East Asian IT services company. Tick has been active since 2018 and targets organizations mostly in Japan but also in South Korea, Russia, and Singapore.
  • LuckyMouse (APT27 and Emissary Panda): On March 1, this cyber-espionage group known to have breached multiple government networks in Central Asia and the Middle East compromised the email server of a governmental entity in the Middle East.
  • Calypso (with ties to Xpath): On March 1, this group compromised the email servers of governmental entities in the Middle East and South America. In the following days, it went on to target organizations in Africa, Asia, and Europe. Calypso targets governmental organizations in these regions.
  • Websiic: On March 1, this APT, which ESET had never seen before, targeted mail servers belonging to seven Asian companies in the IT, telecommunications, and engineering sectors and one governmental body in Eastern Europe.
  • Winnti (aka APT 41 and Barium): Just hours before Microsoft released the emergency patches on March 2, ESET data shows this group compromising the email servers of an oil company and a construction equipment company, both based in East Asia.

ESET said it saw four other groups exploiting the vulnerabilities in the days immediately following Microsoft’s release of the patch on March 2. Two unknown groups started the day after. Two other groups, known as Tonto and Mikroceen, began on March 3 and March 4, respectively.

China and beyond

Joe Slowik, senior security researcher at security firm DomainTools, published his own analysis on Wednesday and noted that three of the APTs that ESET saw exploiting the vulnerabilities ahead of the patches—Tick, Calypso, and Winnti—have previously been linked to hacking sponsored by the People’s Republic of China. Two other APTs that ESET saw exploiting the vulnerabilities a day after the patches—Tonto and Mikroceen—also have ties to the PRC, the researcher said.

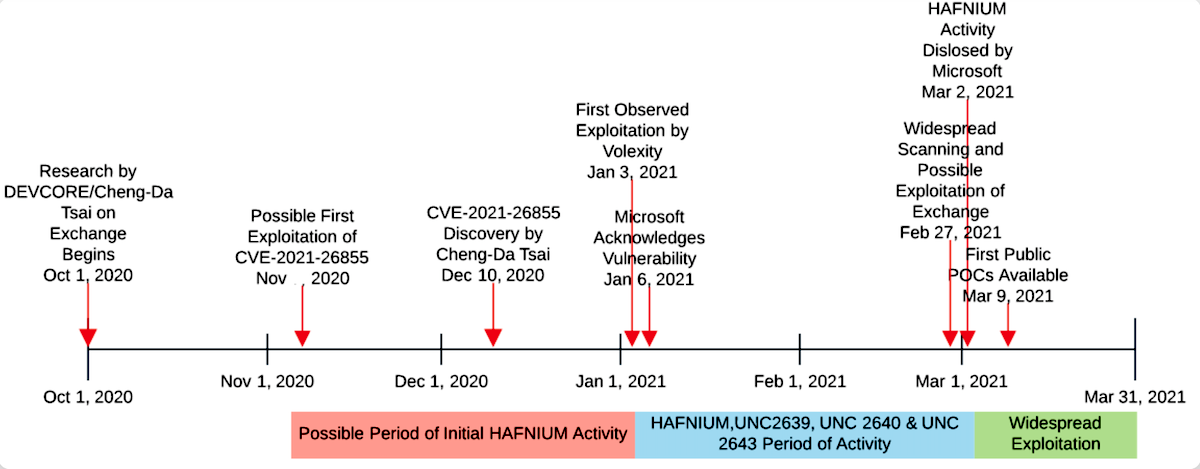
Slowik produced the following timeline:

DomainTools

The timeline includes three exploitation clusters that security firm FireEye has said were exploiting the Exchange vulnerabilities since January. FireEye referred to the groups as UNC2639, UNC2640, and UNC2643 and didn’t tie the clusters to any known APTs or say where they were located.

Because different security firms use different names for the same threat actors, it’s not clear if the groups identified by FireEye overlap with those seen by ESET. If they were distinct, the number of threat actors exploiting the Exchange vulnerabilities prior to a patch would be even higher.

A range of organizations under siege

The tracking of the APTs came as the FBI and the Cybersecurity and Infrastructure Security Agency issued an advisory on Wednesday that said threat groups are exploiting organizations including local governments, academic institutions, non-governmental organizations, and business entities in a range of industries, including agriculture, biotechnology, aerospace, defense, legal services, power utilities, and pharmaceutical.

“This targeting is consistent with previous targeting activity by Chinese cyber actors,” the advisory stated. With security firm Palo Alto Networks reporting on Tuesday that an estimated 125,000 Exchange servers worldwide were vulnerable, CISA and FBI officials’ call for organizations to patch took on an extra measure of urgency.

Both ESET and security firm Red Canary have seen exploited Exchange servers that were infected with DLTMiner, a piece of malware that allows attackers to mine cryptocurrency using the computing power and electricity of infected machines. ESET, however, said it wasn’t clear if the actors behind those infections had actually exploited the vulnerabilities or had simply taken over servers that had already been hacked by someone else.

With so many of the pre-patch exploits coming from groups tied to the Chinese government, the hypothesis from SentinalOne’s Guerrero-Saade—that a PRC entity provided the exploits to multiple hacking groups ahead of the patches—seems to be the simplest explanation. That theory is further supported by two other PRC-related groups—Tonto and Mikroceen—being among the first to exploit the vulnerabilities following Microsoft’s emergency release.

Of course, it’s possible that the half-dozen APTs that exploited the vulnerabilities while they were still zero-days independently discovered the vulnerabilities and developed weaponized exploits. If that’s the case, it’s likely a first, and hopefully a last.

https://arstechnica.com/?p=1748741


Researchers Show First Side-Channel Attack Against Apple M1 Chips

New Browser Side-Channel Attack Doesn’t Require JavaScript

A team of researchers from universities in the United States, Australia and Israel has demonstrated that attackers could launch browser-based side-channel attacks that do not require JavaScript, and they’ve tested the method on a wide range of platforms, including devices that use Apple’s recently introduced M1 chip.

The researchers — representing the Ben-Gurion University of the Negev, the University of Michigan and the University of Adelaide — have published a paper on what they have described as the first browser side-channel attack that uses only CSS and HTML, and works even if JavaScript is completely disabled.

The analysis focused on Prime+Probe, a cache side-channel attack method that can detect which cache sets are accessed by the target and uses that to infer potentially valuable information.

Conducting these types of attacks in the browser typically involves the execution of JavaScript code and timing measurements. Web browsers vendors and third parties have been working on developing protections against such attacks, including by limiting or completely preventing JavaScript execution and by trying to prevent attackers from precisely measuring time.

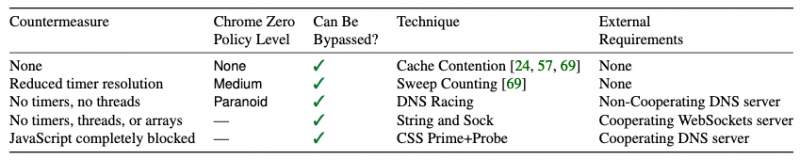
The researchers have developed a sequence of attacks where they have progressively decreased dependency on JavaScript features, which resulted in a method that relies entirely on HTML and CSS. They claim to have shown that all existing countermeasures can be bypassed.

The attack method has been successfully tested — with various levels of success depending on the targeted architecture and existing mitigations — against hardened browser environments (e.g. Tor, Chrome Zero, DeterFox) on devices with Intel, AMD, Samsung and Apple chips.

Side-channel attack test results

Impacted vendors have been notified. Apple told the researchers that the public disclosure of their findings does not raise any concerns.

“We show that advanced variants of the cache contention attack allow Prime+Probe attacks to be mounted through the browser in extremely constrained situations,” the researchers said in their paper. “Cache attacks cannot be prevented by reduced timer resolution, by the abolition of timers, threads, or arrays, or even by completely disabling scripting support. This implies that any secret-bearing process which shares cache resources with a browser connecting to untrusted websites is potentially at risk of exposure.”

Related: New Technique Improves Effectiveness of Timing Channel Attacks

Related: New Side-Channel Attack Targets Intel CPU Ring Interconnect

Related: New Side-Channel Attack Targets OS Page Cache

view counter

Eduard Kovacs (@EduardKovacs) is a contributing editor at SecurityWeek. He worked as a high school IT teacher for two years before starting a career in journalism as Softpedia’s security news reporter. Eduard holds a bachelor’s degree in industrial informatics and a master’s degree in computer techniques applied in electrical engineering.

Previous Columns by Eduard Kovacs:
Tags:

http://feedproxy.google.com/~r/Securityweek/~3/AFzcvAP08tI/researchers-show-first-side-channel-attack-against-apple-m1-chips


Hackers Breach Cameras at Banks, Jails, Tesla and More

A US hacker collective on Tuesday claimed to have tapped into footage from 150,000 security cameras at banks, jails, schools, carmaker Tesla and other sites to expose “the surveillance state.”

Images captured from hacked surveillance video were posted on Twitter with an #OperationPanopticon hashtag.

“What if we just absolutely ended surveillance capitalism in two days?” a purported member of a group called APT-69420 Arson Cats asked amid a string of tweeted images.

“This is the tip of the tip of the tip of the iceberg.”

The hacker group claimed to have ferreted out credentials of an high level administrator account at Silicon Valley firm Verkada, which runs a platform operating security systems online.

“We have disabled all internal administrator accounts to prevent any unauthorized access,” a Verkada spokesperson said in response to an AFP inquiry.

“Our internal security team and external security firm are investigating the scale and scope of this issue, and we have notified law enforcement.”

Verkada added that it has notified companies that rely on its platform.

Surveillance camera imagery posted on Twitter included a jail cell block and a man wearing a fake beard dancing in a bank storage room.

The Verkada breach shows the risk of outsourcing security surveillance to companies in the internet cloud, according to Rick Holland, chief information security officer at Digital Shadows, a risk protection firm.

“Verkada positions itself as a ‘more secure, scalable’ alternative to on-premises network video recorders,” Holland said.

“You don’t always get more secure when you outsource your security to a third party.”

He said he expected the breach to trigger investigations by privacy regulators in the US and Europe.

Related: FBI: Home Surveillance Devices Hacked to Record Swatting Attacks

Related: Apple Awards Researcher $75,000 for Camera Hacking Vulnerabilities

Related: TP-Link Patches Multiple Vulnerabilities in NC Cloud Cameras

view counter

© AFP 2020

Previous Columns by AFP:
Tags:

http://feedproxy.google.com/~r/Securityweek/~3/1ByBStAvxlw/hackers-breach-cameras-banks-jails-tesla-and-more


SAP Patches Critical Flaws in MII, NetWeaver Products

SAP’s March 2021 Security Patch Day updates include 9 new security notes, including two for critical vulnerabilities affecting the company’s NetWeaver Application Server (AS) and Manufacturing Integration and Intelligence (MII) products.

This month’s set of patches also includes 4 updates to previously released Patch Day security notes, including updates for two notes rated Hot News (CVSS score 10), which address a missing authorization check in Solution Manager (CVE-2020-6207) and deliver the latest patches for the Chromium browser in Business Client.

The most severe of the newly released security notes addresses a code injection vulnerability in SAP MII. Tracked as CVE-2021-21480, the vulnerability features a CVSS score of 9.9.

Based on NetWeaver AS Java, SAP MII provides monitoring and data analysis capabilities, capturing data from production machinery and providing real-time information on performance and efficiency.

The critical vulnerability was identified in the Self-Service Composition Environment (SSCE) component, which allows the creation of dashboards (via drag-and-drop) that can be saved as JSP files. The flaw allows an attacker to inject malicious JSP code in a request to the server, which would then be executed when the infected dashboard is opened.

Exploitation of the bug would allow an attacker to access SAP databases and tamper with records, move laterally to other servers, inject malware, and modify network configurations to potentially compromise internal networks.

The second Hot News security note that SAP released on Tuesday addresses a missing authorization check in the Migration Service of NetWeaver AS Java (CVE-2021-21481, CVSS score 9.6).

Used internally to migrate applications between J2EE Engine releases, the service could be abused to gain administrative privileges and potentially fully compromise the vulnerable system. The fix for this vulnerability requires a system restart, Onapsis, a firm that specializes in securing SAP applications, explains.

This month, SAP released a single high-severity security note, to address a possible authentication bypass in HANA LDAP scenarios (CVE-2021-21484, CVSS score 7.7). Successful exploitation requires that the LDAP directory server enables unauthenticated bind and that SAP HANA has been configured to automatically create users and allow access based on LDAP authentication.

All of the remaining security notes included in the March 2021 Security Patch Day are rated medium severity. They address missing authorization checks, an insecure deserialization issue, a reverse TabNabbing vulnerability, improper input validation, and a server-side request forgery bug.

Related: Critical Vulnerability Patched in SAP Commerce Product

Related: Scanning Activity Detected After Release of Exploit for Critical SAP SolMan Flaw

Related: SAP Patches Serious Code Injection, DoS Vulnerabilities

view counter

Ionut Arghire is an international correspondent for SecurityWeek.

Previous Columns by Ionut Arghire:
Tags:

http://feedproxy.google.com/~r/Securityweek/~3/F_swV98_auY/sap-patches-critical-flaws-mii-netweaver-products


Unpatched Flaws in Netgear Business Switches Expose Organizations to Attacks

Security researchers have identified multiple vulnerabilities in ProSAFE Plus JGS516PE and GS116Ev2 business switches from Netgear, the most severe of which could allow a remote, unauthenticated attacker to execute arbitrary code.

A total of 15 vulnerabilities affecting Netgear switches that use the ProSAFE Plus configuration utility were found to expose users to various risks, according to researchers with IT security firm NCC Group.

The most important of these bugs is CVE-2020-26919, an unauthenticated remote code execution flaw rated critical severity (CVSS score of 9.8).

Affecting firmware versions prior to 2.6.0.43, the bug is related to the internal management web application not implementing the correct access controls, which could allow attackers to bypass authentication and run code with the privileges of the administrator.

“Due to the ability of execute system commands through the ‘debug’ web sections, a successful exploitation of this vulnerability can lead to remote code execution on the affected device,” NCC Group notes.

The researchers also discovered that the Netgear Switch Discovery Protocol (NSDP), a network protocol functioning as a discovery method that also allows for switch management, fails to properly handle authentication packages, thus leading to authentication bypasses (CVE-2020-35231, CVSS score of 8.8).

An attacker able to exploit this vulnerability “could execute any management actions in the device, including wiping the configuration by executing a factory restoration,” the researchers say.

NCC Group says that Netgear has informed them that the NSDP has reached end of life (EOL) and that none of the issues identified in it will be addressed. Users are advised to disable the remote management feature.

“Netgear reported that most of the vulnerabilities affecting the NSDP protocol were known due to end-of-life years ago and it is still enabled for legacy reasons, for customers who preferred to use Prosafe Plus. Furthermore, we were informed that, due to hardware limitations, it is not possible to implement many of the standard encryption protocols, such as those needed to implement HTTPS,” NCC Group notes.

The researchers also found issues with the firmware update mechanism on the vulnerable switches. One of them, CVE-2020-35220 (CVSS score of 8.3), could allow attackers to upload custom firmware files without administrative rights.

The second issue (CVE-2020-35232, CVSS score of 8.1) resides in the improper implementation of internal checks, which could allow attackers to craft firmware files that could “overwrite the entire memory with custom code.”

Other high-severity vulnerabilities in Netgear’s switches could lead to denial of service (CVE-2020-35224, CVSS score 8.1), or could allow an attacker to generate valid passwords (CVE-2020-35221, CVSS score 7.5) or perform requests using a single authenticated packet (CVE-2020-35229, CVSS score 7.5).

A stored XSS issue in language settings (CVE-2020-35228, CVSS score 7.2) could be abused to inject JavaScript code that would be executed on all webpages, while a buffer overflow (CVE-2020-35227, CVSS score 7.2) could be abused to cause a system reboot, among others.

Another vulnerability in the NSDP protocol, the researchers discovered, could be abused to retrieve the DHCP status without authentication, thus allowing remote users to configure the service, likely leading to denial of service (CVE-2020-35226, CVSS score 7.1).

The security researchers also identified a series of medium-severity flaws, such as unauthenticated access to switch configuration parameters (CVE-2020-35222), TFTP unexpected behavior (CVE-2020-35233), integer overflow instances (CVE-2020-35230), write command buffer overflows (CVE-2020-35225), and ineffective cross-site request forgery protections (CVE-2020-35223).

In December 2020, Netgear released firmware version 2.6.0.48, which includes patches for CVE-2020-35220, CVE-2020-35232, CVE-2020-35233, and other issues. The remaining issues won’t receive patches, the researchers say.

Related: NETGEAR Router, WD NAS Device Hacked on First Day of Pwn2Own Tokyo 2020

Related: Netgear Starts Patching Serious Vulnerabilities Affecting Tens of Products

Related: Senator Urges Vendors to Secure Networking Devices Amid COVID-19 Outbreak

view counter

Ionut Arghire is an international correspondent for SecurityWeek.

Previous Columns by Ionut Arghire:
Tags:

http://feedproxy.google.com/~r/Securityweek/~3/LzZrWK1srh8/unpatched-flaws-netgear-business-switches-expose-organizations-attacks


Critical 0-day that targeted security researchers gets a patch from Microsoft

Shadowy figures stand beneath a Microsoft logo on a faux wood wall.

Microsoft has patched a critical zero-day vulnerability that North Korean hackers were using to target security researchers with malware.

The in-the-wild attacks came to light in January in posts from Google and Microsoft. Hackers backed by the North Korean government, both posts said, spent weeks developing working relationships with security researchers. To win the researchers’ trust, the hackers created a research blog and Twitter personas who contacted researchers to ask if they wanted to collaborate on a project.

Eventually, the fake Twitter profiles asked the researchers to use Internet Explorer to open a webpage. Those who took the bait would find that their fully patched Windows 10 machine installed a malicious service and an in-memory backdoor that contacted a hacker-controlled server.

Microsoft on Tuesday patched the vulnerability. CVE-2021-26411, as the security flaw is tracked, is rated critical and requires only low-complexity attack code to exploit.

From rags to riches

Google said only that the people who reached out to the researchers worked for the North Korean government. Microsoft said they were part of Zinc, Microsoft’s name for a threat group that is better known as Lazarus. Over the past decade, Lazarus has transformed from a ragtag group of hackers to what can often be a formidable threat actor.

A United Nations report from 2019 reportedly estimated Lazarus and associated groups have generated $2 billion for the country’s weapons of mass destruction programs. Lazarus has also been tied to the Wannacry worm that shut down computers around the world, fileless Mac malware, malware that targets ATMs, and malicious Google Play apps that targeted defectors.

Besides using the watering-hole attack that exploited IE, the Lazarus hackers who targeted the researchers also sent targets a Visual Studio Project purportedly containing source code for a proof-of-concept exploit. Stashed inside the project was custom malware that contacted the attackers’ control server.

While Microsoft describes CVE-2021-26411 as an “Internet Explorer Memory Corruption Vulnerability,” Monday’s advisory says the vulnerability also affects Edge, a browser Microsoft built from scratch that’s considerably more secure than IE. The vulnerability retains its critical rating for Edge, but there are no reports that exploits have actively targeted users of that browser.

The patch came as part of Microsoft’s Update Tuesday. In all, Microsoft issued 89 patches. Besides the IE vulnerability, a separate escalation privilege flaw in the Win32k component is also under active exploit. Patches will install automatically over the next day or two. Those who want the updates immediately should go to Start > settings (the gear icon) > Update & Security > Windows Update.

https://arstechnica.com/?p=1748406


Tens of thousands of US organizations hit in ongoing Microsoft Exchange hack

A stylized skull and crossbones made out of ones and zeroes.

Tens of thousands of US-based organizations are running Microsoft Exchange servers that have been backdoored by threat actors who are stealing administrator passwords and exploiting critical vulnerabilities in the email and calendaring application, it was widely reported. Microsoft issued emergency patches on Tuesday, but they do nothing to disinfect systems that are already compromised.

KrebsOnSecurity was the first to report the mass hack. Citing multiple unnamed people, reporter Brian Krebs put the number of compromised US organizations at at least 30,000. Worldwide, Krebs said there were at least 100,000 hacked organizations. Other news outlets, also citing unnamed sources, quickly followed with posts reporting the hack had hit tens of thousands of organizations in the US.

Assume compromise

“This is the real deal,” Chris Krebs, the former head of the Cybersecurity and Infrastructure Security Agency, said on Twitter, referring to the attacks on on-premisis Exchange, which is also known as Outlook Web Access. “If your organization runs an OWA server exposed to the internet, assume compromise between 02/26-03/03.” His comments accompanied a Tweet on Thursday from Jake Sullivan, the White House national security advisor to President Biden.

Hafnium has company

Microsoft on Tuesday said on-premises Exchange servers were being hacked in “limited targeted attacks” by a China-based hacking group the software maker is calling Hafnium. Following Friday’s post from Brian Krebs, Microsoft updated its post to say that it was seeing “increased use of these vulnerabilities in attacks targeting unpatched systems by multiple malicious actors beyond HAFNIUM.”

Katie Nickels, director of intelligence at security firm Red Canary, told Ars that her team has found Exchange servers that were compromised by hackers using tactics, techniques, and procedures that are distinctly different than those used by the Hafnium group Microsoft named. She said Red Canary has counted five “clusters that look differently from each other, [though] telling if the people behind those are different or not is really challenging and unclear right now.”

On Twitter, Red Canary said that some of the compromised Exchange servers the company has tracked ran malware that fellow security firm Carbon Black analyzed in 2019. The malware was part of an attack that installed cryptomining software called DLTminer. It’s unlikely Hafnium would install a payload like that.

Microsoft said that Hafnium is a skilled hacking group from China that focuses primarily on stealing data from US-based infectious disease researchers, law firms, higher-education institutions, defense contractors, policy think tanks, and nongovernmental organizations. The group, Microsoft said, was hacking servers by either exploiting the recently fixed zeroday vulnerabilities or by using compromised administrator credentials.

It’s not clear what percentage of infected servers are the work of Hafnium. Microsoft on Tuesday warned that the ease of exploiting the vulnerabilities made it likely other hack groups would soon join Hafnium. If ransomware groups aren’t yet among the clusters compromising servers, it’s almost inevitable that they soon will be.

Backdooring servers

Brian Krebs and others reported that tens of thousands of Exchange servers had been compromised with a webshell, which hackers install once they’ve gained access to a server. The software allows attackers to enter administrative commands through a terminal Window that’s accessed through a web browser.

Researchers have been careful to note that simply installing the patches Microsoft issued in Tuesday’s emergency release would do nothing to disinfect servers that have already been backdoored. The webshells and any other malicious software that have been installed will persist until it is actively removed, ideally by completely rebuilding the server.

People who administer Exchange servers in their networks should drop whatever they’re doing right now and carefully inspect their machines for signs of compromise. Microsoft has listed indicators of compromise here. Admins can also use this script from Microsoft to test if their environments are affected.

This week’s escalation of Exchange server hacks comes three months after security professionals uncovered the hack of at least nine federal agencies and about 100 companies. The primary vector for infections was through software updates from network tools maker SolarWinds. The mass hack was one of—if not the—the worst computer intrusions in US history. It’s possible the Exchange Server will soon claim that distinction.

There’s still much that remains unknown. For now, people would do well to follow Chris Krebs’ advice to assume on-premises servers are compromised and act accordingly.

https://arstechnica.com/?p=1747745


Microsoft Shares Additional Mitigations for Exchange Server Vulnerabilities Under Attack

Microsoft on Friday released alternative mitigation measures for organizations who have not been able to immediately apply emergency out-of-band patches released earlier this week that address vulnerabilities being exploited to siphon e-mail data from corporate Microsoft Exchange servers.

“These mitigations are not a remediation if your Exchange servers have already been compromised, nor are they full protection against attack,” Microsoft warned in a blog post. “We strongly recommend investigating your Exchange deployments using the hunting recommendations here to ensure that they have not been compromised. We recommend initiating an investigation in parallel with or after applying one of the following mitigation strategies.”

Microsoft also provided a nmap script to help customers discover vulnerable servers within their infrastructure.

Security researchers have warned that multiple cyber-espionage groups have been targeting vulnerable Exchange servers. Some reports suggest that 30,000 or more organizations may have been hacked via the Exchange security holes.

Analysts say that HAFNIUM, a state-sponsored hacking group operating out of China, has been on an an active hacking spree with a massive espionage campaign underway to siphon data from organizations globally.

“This is the real deal. If your organization runs an OWA server exposed to the internet, assume compromise between 02/26-03/03,” Ex-CISA Chief Chris Krebs tweeted. “Check for 8 character aspx files in C:\\inetpub\wwwroot\aspnet_client\system_web\. If you get a hit on that search, you’re now in incident response mode.”

The U.S. Cybersecurity and Infrastructure Security (CISA) also issued an alert Friday, urging organizations to upgrade their on-premises Microsoft Exchange servers to the latest supported version.

Cybersecurity firm Volexity, which was credited by Microsoft for reporting different parts of the attack chain, has published a blog post with technical details and a video demonstrating exploitation in action, along with known attacker IP addresses connected to the attacks. Volexity said it detected anomalous activity from two of its customers’ Microsoft Exchange servers in January 2021, which led to discovery of the attacks.

“This is an active threat,” White House press secretary Jennifer Psaki said in a press briefing Friday. “Everyone running these servers needs to act now to patch them. We are concerned that there are a large number of victims and are working with our partners to understand the scope of this.”
view counter

For more than 10 years, Mike Lennon has been closely monitoring the threat landscape and analyzing trends in the National Security and enterprise cybersecurity space. In his role at SecurityWeek, he oversees the editorial direction of the publication and is the Director of several leading security industry conferences around the world.

Previous Columns by Mike Lennon:
Tags:

http://feedproxy.google.com/~r/Securityweek/~3/IihaWmU26H4/microsoft-shares-additional-mitigations-exchange-server-vulnerabilities-under-attack


Supermicro, Pulse Secure Respond to Trickbot’s Ability to Target Firmware

Server and storage technology giant Supermicro and secure access solutions provider Pulse Secure have issued advisories to inform users that some of their products are vulnerable to the Trickbot malware’s ability to target firmware.

In early December, security researchers at Advanced Intelligence (AdvIntel) and enterprise device security firm Eclypsium revealed that Trickbot not only survived a takedown attempt, but also gained the ability to scan UEFI/BIOS firmware for vulnerabilities that would allow making modifications.

Referred to as Trickboot, the ability would enable TrickBot operators to use firmware implants and backdoors in their attacks, control the boot operations to fully control systems, or even start bricking devices, the researchers warned at the time.

“TrickBoot is a new functionality within the TrickBot malware toolset capable of discovering vulnerabilities and enabling attackers to read/write/erase the device’s BIOS,” Supermicro notes in an advisory published this week.

The malware can check if the BIOS control register is unlocked and if modifications could be made to the BIOS region contents, and then implant malicious code that would survive OS reinstalls.

Supermicro said the vulnerability affects a subset of the X10 UP motherboards and that a mitigation will be provided. However, only products that have not reached end of life (EOL) will automatically receive the BIOS update. Patches for EOL products will be provided at request.

“A vulnerability in the BIOS of Pulse Secure (PSA-Series Hardware) could allow an attacker to compromise BIOS firmware. This vulnerability can be exploited only as part of an attack chain. Before an attacker can compromise the BIOS, they must exploit the device,” Pulse Secure notes in its advisory.

The company says that only two of its device models are affected, namely PSA-5000 and PSA-7000. Patches are available for Pulse Connect Secure / Pulse Policy Secure and are pending release for Pulse One (the on-prem appliance only).

Related: NSA Publishes Guidance on UEFI Secure Boot Customization

Related: TrickBot Gets Updated to Survive Takedown Attempts

Related: New Dell Utility Alerts Security Teams of BIOS Attacks

view counter

Ionut Arghire is an international correspondent for SecurityWeek.

Previous Columns by Ionut Arghire:
Tags:

http://feedproxy.google.com/~r/Securityweek/~3/dVRnmu8xB50/supermicro-pulse-secure-respond-trickbots-ability-target-firmware